Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

Mutt

rah

Consulting &

ISO Certifications

-ISO Certification-

ISO 27701 Certification Services in Muttrah

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

Leading Muttrah provider of ISO 27701 certification services, Qualitcert specializes in helping businesses set up strong privacy information management systems (PIMS) that meet ISO 27701 requirements. This standard, which builds upon the structure of ISO 27001, is centered on handling personal data and making sure that laws like the GDPR governing data protection are followed. Throughout the certification process, Qualitcert’s team of knowledgeable consultants provides complete support, doing risk assessments, creating privacy policies, and putting in place efficient procedures to protect personal data. In order to improve staff awareness of privacy issues and acceptable practices, they also offer customized training programs. Organizations in Muttrah can show their dedication to safeguarding personal data, gain the trust of customers, and improve their brand by obtaining ISO 27701 certification under the direction of Qualitcert.

Please Reach Us Today

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

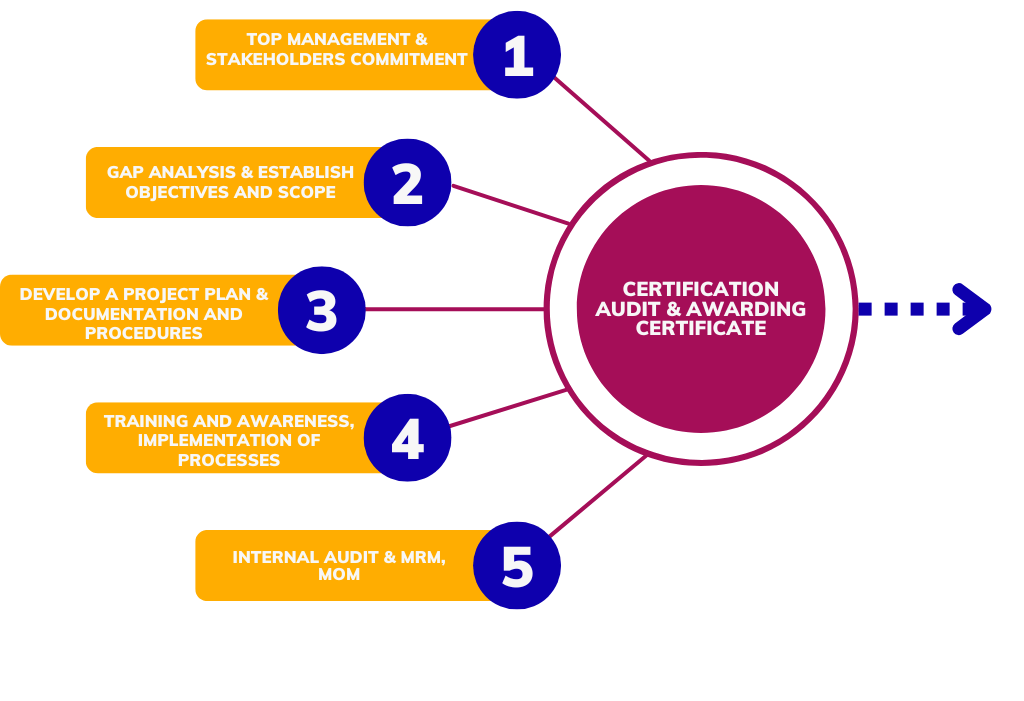
Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
ISO/IEC 27701 in Muttrah

ISO/IEC 27701 Services in Muttrah for Accountable privacy information management

Privacy management in Muttrah becomes much easier when the organisation can trace personal information from collection through use, sharing, retention and deletion. A detailed privacy notice does not compensate for missing PII inventories, unclear controller-processor roles or inconsistent supplier and retention controls.

Map the personal-data journey before adding privacy paperwork

The operating design needs to connect PII inventory, data flows and controller-processor roles with privacy risk, retention and rights and supplier privacy; otherwise individual controls can appear complete while the overall outcome remains weak.

Privacy management in Muttrah becomes much easier when the organisation can trace personal information from collection through use, sharing, retention and deletion; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

Qualitcert can support the organisation in turning privacy information management into responsibilities, evidence, internal review and improvement actions that fit actual Muttrah operations.

A detailed privacy notice does not compensate for missing PII inventories, unclear controller-processor roles or inconsistent supplier and retention controls; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

Operating Context in Muttrah

Privacy exposure becomes clearer when data flows are visible

The controls need to fit real handoffs, suppliers, technology and operating conditions rather than an abstract model; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

Results from supplier privacy should lead to a decision, correction or improvement instead of being recorded without changing how the process is managed.

Ownership of PII inventory should remain visible whenever work crosses teams, systems or external providers; unclear handoffs can weaken an otherwise well-designed control.

Controller-processor roles needs an explicit trigger for reassessment when risk, technology, suppliers, workload or stakeholder needs change.

Practical Value of ISO/IEC 27701

What stronger privacy management changes in daily processing

The business value comes from stronger privacy information management and clearer decisions, not from increasing document volume.

Ownership of PII inventory becomes clearer

Decision rights and review points make PII inventory less dependent on informal knowledge.

Data flows becomes more consistent — focused on privacy information management — applied to the current operating model

Current records and agreed criteria make data flows easier to compare over time.

Decisions around privacy risk become easier to defend

Risk, exceptions and changing conditions are considered before privacy risk is treated as routine.

Supplier privacy produces visible follow-through — focused on privacy information management — applied to the current operating model

Results are converted into actions, learning or management decisions rather than passive records; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

Applications Across Muttrah

Muttrah organisations handling different categories and flows of PII

Different sectors need different examples, evidence and control depth even when they use the same framework; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

01

Hotels — privacy information management application

In Muttrah, hotels can use ISO/IEC 27701 to manage guest, booking and marketing information across providers; the controls should follow the real workflow and the consequence of failure in that environment.

02

Healthcare — privacy information management application

In Muttrah, healthcare can use ISO/IEC 27701 to govern sensitive personal information and outsourced processing; the controls should follow the real workflow and the consequence of failure in that environment.

03

Education providers — privacy information management application

In Muttrah, education providers can use ISO/IEC 27701 to control learner, guardian and employee data; the controls should follow the real workflow and the consequence of failure in that environment.

04

Technology firms — privacy information management application

In Muttrah, technology firms can use ISO/IEC 27701 to clarify processor and subprocessor obligations; the controls should follow the real workflow and the consequence of failure in that environment.

05

Retail and e-commerce — privacy information management application

In Muttrah, retail and e-commerce can use ISO/IEC 27701 to manage customer profiles, orders and marketing data; the controls should follow the real workflow and the consequence of failure in that environment.

06

HR services — privacy information management application

In Muttrah, hr services can use ISO/IEC 27701 to control employee data, retention and external processing; the controls should follow the real workflow and the consequence of failure in that environment.

How ISO/IEC 27701 Works in Practice

Follow personal information from collection through deletion

This sequence follows the specific control logic of ISO/IEC 27701 rather than a generic readiness routine.

01

Identify the boundary for PII inventory

Name the accountable owner, intended result and decision authority for PII inventory.

02

Confirm how data flows works today

Use current records and interviews to understand how data flows behaves in real work.

03

Design criteria for controller-processor roles

Make choices around controller-processor roles repeatable by defining criteria and escalation.

04

Implement privacy risk through normal responsibilities

Embed privacy risk in everyday roles instead of a separate audit-only routine.

05

Audit evidence around retention and rights

Monitor retention and rights, retain exceptions and verify that follow-up happens.

06

Correct the system using supplier privacy

Use supplier privacy to decide whether correction, resources or a broader change is required.

Evidence That Matters

Records that make privacy information management understandable without reconstruction

Evidence should be current, attributable and tied to an actual decision, activity or exception; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

Operating evidence for ISO/IEC 27701 in Muttrah

  • PIMS scope, showing the approved boundary and current owner
  • PII inventory, with responsibilities and review status visible
  • Data-flow maps, linked to actual operating decisions
  • Role register, showing how changes are approved
  • Privacy risk assessment, supported by implementation evidence
  • Processing purposes, with current monitoring or evaluation results
  • Retention schedule, showing relevant approvals and exceptions
  • Supplier assessments, retained for traceability and follow-up; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.
  • Rights-request log, connected to corrective or improvement actions
  • Management review, used as an input to leadership review; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.
For ISO/IEC 27701, process owners should be able to explain why each record exists and which decision or control it supports.

Weak points that deserve attention before formal review — focused on privacy information management — applied to the current operating model

For ISO/IEC 27701, these patterns can make documented expectations look stronger than everyday practice.

  • Privacy notices exist without a complete PII inventory. The issue may remain hidden until a real exception occurs.
  • Processing roles are assumed rather than mapped. That often creates inconsistent evidence between people or shifts.
  • Retention schedules are not implemented in systems. Management then has less reliable information for decisions.
  • Suppliers receive PII before due diligence. The control may exist without a clear measure of effectiveness.
  • Rights requests are handled inconsistently. The same weakness can return because the underlying cause remains.
Closing these ISO/IEC 27701 weaknesses early improves the operating system and reduces last-minute evidence repair.
Related Management Areas

Where the same process also depends on broader management controls, consider for ISO/IEC 27701 ISO/IEC 27001 in Muttrah.

A second discipline that can strengthen connected responsibilities is for ISO/IEC 27701 SOC 2 in Muttrah.

For another governance or assurance perspective, review for ISO/IEC 27701 ISO 31000 in Muttrah.

ISO/IEC 27701 Questions

Questions process owners should answer with real ISO/IEC 27701 evidence

These questions test whether ISO/IEC 27701 is understood, operated and reviewed during normal work.

What should a Muttrah organisation define first for ISO/IEC 27701?

Define scope, intended outcomes, key stakeholders and the operating processes that influence privacy information management; this creates a practical boundary for ownership and evidence.

Who should own PII inventory in the ISO/IEC 27701 operating context for Muttrah?

Ownership should sit with someone able to influence the process, make or escalate decisions and keep evidence for PII inventory current.

What evidence shows data flows is working?

Use recent approvals, monitoring results, exceptions and follow-up connected to data flows; the strongest evidence is produced during normal work.

When should controller-processor roles be reconsidered?

Review controller-processor roles when significant changes in risk, technology, suppliers, workforce, customer need or operating conditions could affect the original decision.

Why is privacy risk important to ISO/IEC 27701?

Privacy risk directly supports privacy information management; the organisation should be able to explain the outcome it protects and how effectiveness is checked.

How can retention and rights be controlled without unnecessary paperwork?

Keep only the documented information needed to make retention and rights repeatable, reviewable and proportionate to risk; reuse effective operating records wherever possible.

What should internal review test about supplier privacy in the ISO/IEC 27701 operating context for Muttrah?

Sample supplier privacy in real operation, examine exceptions and verify that follow-up addresses causes rather than only closing tasks.

How should external providers be considered within ISO/IEC 27701 in the ISO/IEC 27701 operating context for Muttrah?

External providers should be controlled according to how strongly they can affect privacy information management, with approval, monitoring and escalation matched to that exposure.

What should management decide after reviewing ISO/IEC 27701 performance in the ISO/IEC 27701 operating context for Muttrah?

Management should decide on unresolved risks, resources, changes and improvement priorities rather than simply acknowledge performance information; for ISO/IEC 27701 in Muttrah, this point is applied to the current operating model.

How can Qualitcert support ISO/IEC 27701 in Muttrah in the ISO/IEC 27701 operating context for Muttrah?

Qualitcert can support gap assessment, implementation planning, control design, internal audit, evidence review and readiness activities relevant to ISO/IEC 27701.

Next Step with ISO/IEC 27701

Choose one personal-data flow and make every handoff accountable

Choose one material area—supplier privacy—and follow it from ownership through criteria, evidence, exceptions and improvement decisions.

View ISO/IEC 27701 Services in Muttrah — ISO/IEC 27701 Muttrah →
Scroll to Top