
ISO Certifications
Chen
nai
Consulting &
ISO Certifications
-ISO Certification-
QUALIT
CERT
VAPT Certification & Consulting Company in Chennai
Qualitcert is a distinguished provider of VAPT (Vulnerability Assessment and Penetration Testing) certification services in Chennai, India, offering comprehensive solutions to bolster cybersecurity defenses for organizations. Specializing in identifying vulnerabilities and strengthening security measures, Qualitcert’s VAPT services encompass thorough assessments, penetration testing, and strategic consulting to mitigate risks effectively. Their team of skilled cybersecurity professionals utilizes cutting-edge tools and methodologies to conduct comprehensive assessments, identifying potential weaknesses in networks, systems, and applications. Through meticulous analysis and strategic guidance, Qualitcert empowers organizations to proactively address vulnerabilities, enhance their security posture, and safeguard against cyber threats. Trusted for their expertise, reliability, and commitment to client success, Qualitcert stands as a trusted partner for organizations in Chennai seeking to fortify their cybersecurity defenses through VAPT certification and consulting services.
Get In Touch
Approach and Methodology used to implement Management System Standard
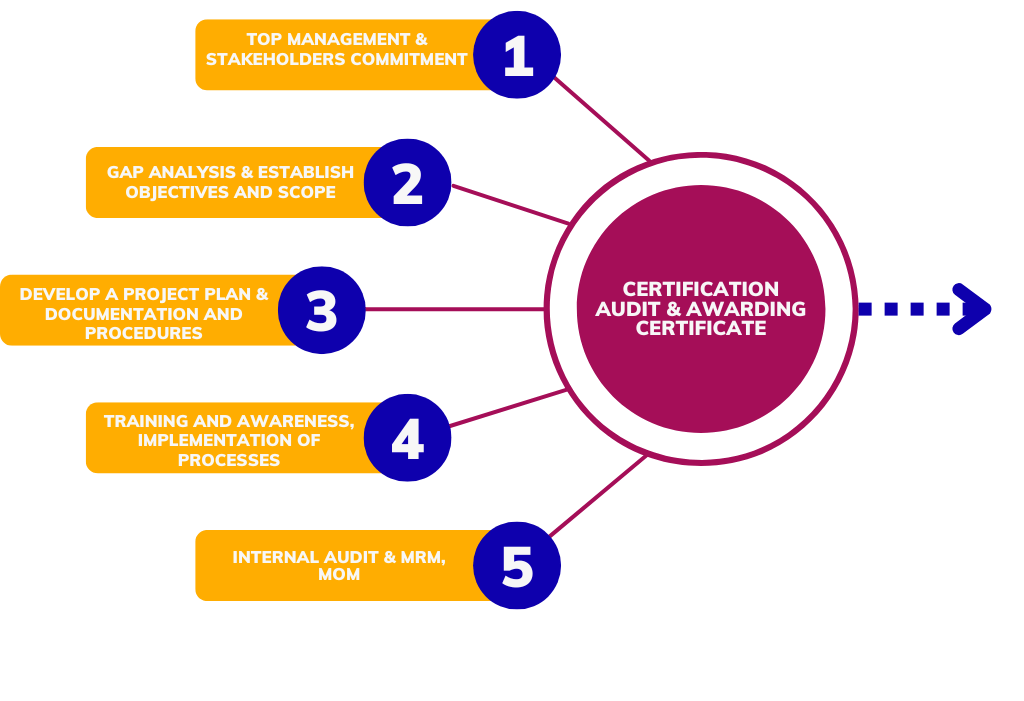
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
VAPT Services in Chennai
Identify vulnerabilities, validate exploitable attack paths and confirm remediation through a scoped programme of assessment, penetration testing and retesting.
Find Weaknesses and Prove Which Ones Matter
Vulnerability Assessment and Penetration Testing combines breadth with depth. Automated and manual techniques identify weaknesses, while controlled exploitation demonstrates realistic impact.
Qualitcert helps Chennai organisations define scope, rules of engagement, test environments, credentials, exclusions and communication procedures before testing begins.
Testing can cover external infrastructure, internal networks, web applications, mobile applications, APIs, cloud environments and selected wireless or operational-technology components.
Reports separate evidence from assumptions, explain risk in business terms, provide remediation guidance and support retesting after corrective action.
Technical Validation for Chennai's Connected Systems
Digital products, customer portals, payment interfaces, cloud workloads and industrial networks create attack surfaces that cannot be assessed through policy review alone.
Vulnerability scanning can identify known issues, but manual testing is often needed to understand chained weaknesses, broken access control, business-logic abuse and misconfiguration.
A controlled VAPT engagement provides technical evidence without disrupting operations and helps teams prioritise remediation based on exploitability and impact.
Qualitcert establishes clear authorisation, safe testing procedures, escalation routes and retesting criteria.
What disciplined VAPT provides
The value comes from validated findings and clear remediation priorities rather than raw vulnerability counts.
Verified technical risk
Manual testing separates exploitable issues from false positives and low-value scanner noise.
Prioritised remediation
Severity, exposure, exploitability and business impact guide practical action sequencing.
Stronger customer assurance
Reports and retest evidence support due diligence, compliance and contractual security expectations.
Improved engineering feedback
Root causes and attack paths help development and infrastructure teams prevent recurrence.
VAPT applications for organisations in Chennai
The testing method should match the asset type, threat model, authentication level and operational sensitivity.
Web and SaaS Applications
Test authentication, authorisation, session handling, input validation, configuration and business logic.
Mobile Applications and APIs
Assess application storage, transport, API access, token handling and backend controls.
Cloud Environments
Review exposed services, identity permissions, storage, segmentation, secrets and configuration weaknesses.
Corporate Networks
Identify exploitable systems, weak services, credential paths, segmentation gaps and privilege escalation.
Fintech and Payment Interfaces
Test externally exposed services, APIs, access controls and transaction-related attack paths.
Industrial and IoT Environments
Assess connected devices, remote access, network boundaries and selected technical exposures under agreed safeguards.
A controlled route from scope to retest
The engagement protects operational stability while producing reproducible and decision-ready evidence.
Authorise and scope
Define assets, dates, methods, credentials, exclusions, contacts, data handling and stop conditions.
Discover the attack surface
Identify reachable hosts, services, applications, APIs, versions and exposed functionality.
Assess vulnerabilities
Use appropriate tools and manual analysis to identify configuration, code and control weaknesses.
Validate exploitation safely
Confirm material findings and attack paths without exceeding agreed operational limits.
Report and remediate
Document evidence, impact, severity, root cause and prioritised corrective recommendations.
Retest closed findings
Verify remediation, identify residual exposure and issue updated status evidence.
Technical records expected from a professional engagement
Deliverables should be suitable for executives, risk owners and technical teams without exposing unnecessary sensitive detail.
Typical VAPT documentation
- Signed rules of engagement
- Authorised asset list
- Testing methodology
- Credential and access plan
- Finding evidence
- Risk and severity rationale
- Executive summary
- Technical remediation guidance
- Finding owner tracker
- Retest confirmation report
Security testing mistakes
Poorly planned testing can produce misleading results or unnecessary operational risk.
- Running scans without written authorisation and scope boundaries.
- Calling automated scanning a full penetration test.
- Testing only IP addresses while ignoring applications and APIs.
- Ranking findings by scanner score without business context.
- Closing findings from screenshots without a controlled retest.
Related VAPT Services for Chennai Organisations
For a connected requirement, review ISO/IEC 27001 services in Chennai to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review SOC 2 services in Chennai where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review ISO 9001 services in Chennai to reduce duplicated work and build a coherent assurance programme.
VAPT questions from organisations in Chennai
These answers explain scope, scanning, penetration testing, reporting and remediation.
What is the difference between vulnerability assessment and penetration testing?
Vulnerability assessment identifies potential weaknesses, while penetration testing manually validates exploitability and attack impact within authorised limits.
Is an automated scan enough for VAPT?
No. Automated tools are useful, but professional testing includes manual verification, logic testing, attack-path analysis and false-positive review.
What systems can be included in VAPT?
Scope may include external or internal networks, web applications, APIs, mobile apps, cloud environments and wireless systems.
Is VAPT safe for production systems?
It can be performed safely with agreed methods, timing, stop conditions and exclusions, but residual operational risk must be assessed before testing.
What is authenticated vulnerability testing?
It uses approved credentials to inspect patching, configurations and privileges that cannot be assessed accurately from an unauthenticated position.
How are vulnerabilities prioritised?
Priority should consider technical severity, exposure, exploitability, affected data or service, compensating controls and business impact.
What should a penetration-test report contain?
It should include scope, methodology, executive findings, technical evidence, risk rationale, remediation guidance and limitations.
Why is retesting important?
Retesting confirms that the specific weakness and related attack path were removed rather than relying only on implementation statements.
How often should VAPT be performed?
Frequency should reflect risk, system change, contractual obligations and threat exposure. Major changes can trigger testing outside the routine cycle.
How does Qualitcert support VAPT in Chennai?
Qualitcert can help define scope, coordinate testing, present prioritised findings, support remediation tracking and verify closure through retesting.
Scope a Safe and Actionable VAPT Engagement in Chennai
Share the systems, environments and assurance objective. Qualitcert will define the test scope, rules of engagement, reporting approach and retest plan.