
Chennai
QUALIT
CERT
Qualitcert, a leading certification and consulting service provider, offers specialized support for ISO 27001 certification in Chennai, India. Focused on information security management systems (ISMS), Qualitcert assists organizations in implementing robust frameworks aligned with ISO 27001 standards. Their comprehensive approach involves thorough assessment of information security risks, documentation support, and implementation of security controls to ensure compliance and continual improvement in information security practices. With expert guidance from Qualitcert consultants, businesses in Chennai receive tailored solutions to enhance data protection, meet regulatory requirements, and achieve ISO 27001 certification efficiently. Through their commitment to excellence in information security management, Qualitcert empowers organizations in Chennai to safeguard their sensitive information, build trust with stakeholders, and mitigate cybersecurity risks effectively.
Get In Touch
Approach and Methodology used to implement Management System Standard
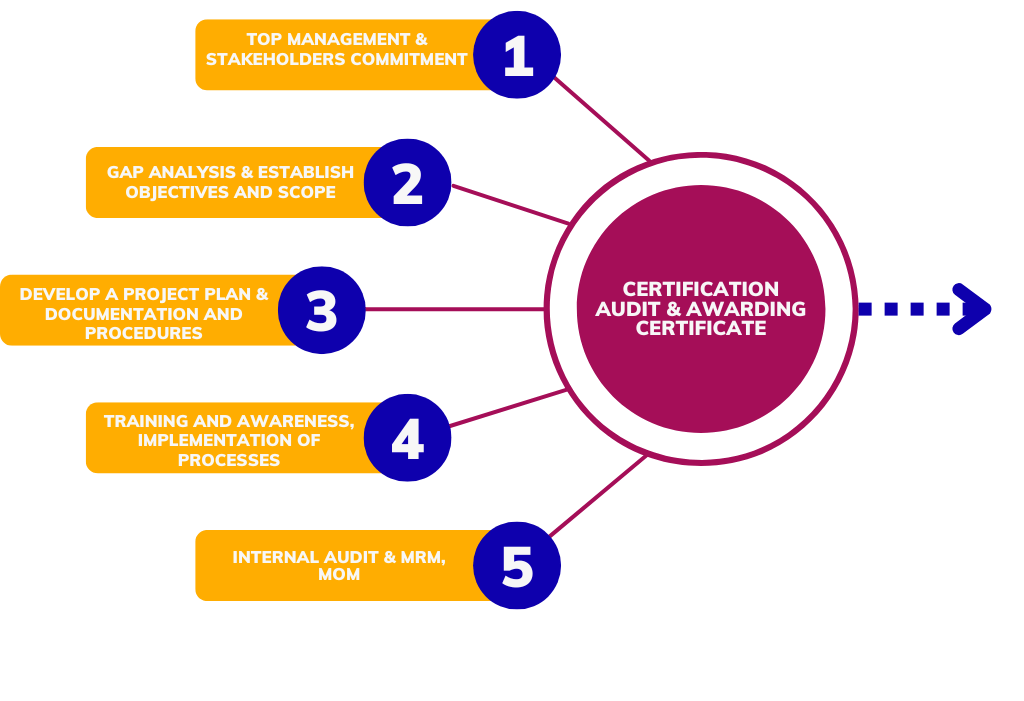
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
ISO 27001 Certification Consulting in Chennai
Build a risk-based information security management system with a clear scope, defensible risk treatment, an accurate Statement of Applicability and effective Annex A controls.
Create an ISMS That Connects Risk Decisions to Evidence
ISO/IEC 27001 is not a checklist of security technologies. It is a management system for deciding what information must be protected, understanding relevant threats and vulnerabilities, and selecting proportionate controls.
Qualitcert helps Chennai organisations define the ISMS scope, identify information assets and interested-party requirements, assess risk and document treatment decisions.
The Statement of Applicability is developed as a reasoned record of which Annex A controls apply, how they are implemented and why any exclusions are justified.
Policies, procedures, technical evidence, supplier controls, incident management, internal audit and management review are then aligned so the organisation can demonstrate that the ISMS operates over time.
Protecting Data Across Chennai's Technology and Service Ecosystem
Technology companies, BPO providers, manufacturers, financial platforms and healthcare organisations in Chennai often process sensitive information across cloud, office, remote-work and supplier environments.
Security obligations may come from customers, contracts, privacy expectations, sector rules and internal risk appetite. Without an ISMS, these demands can lead to duplicated questionnaires and inconsistent control ownership.
ISO 27001 provides a common governance structure for access, cryptography, secure development, logging, resilience, supplier security, physical protection and incident response.
Qualitcert focuses on traceable risk decisions and operating evidence, helping leadership understand residual risk rather than relying on policy documents alone.
How ISO 27001 supports trust and resilience
The value lies in making security decisions traceable, risk-based and repeatable across business and technical teams.
Better risk ownership
Business owners can see residual risk, treatment status and the decisions requiring acceptance or investment.
Stronger customer assurance
Controlled evidence supports due diligence, tenders and security reviews from clients and partners.
More coordinated incident response
Roles, escalation, evidence handling and lessons learned are planned before a security event occurs.
Improved supplier governance
Security expectations, assessments and monitoring are aligned with the information and services entrusted to third parties.
ISO 27001 applications in Chennai' service economy
The scope and controls should reflect information flows, technology dependencies and contractual commitments.
Software and SaaS Providers
Govern secure development, cloud access, tenant data, deployment, logging and incident response.
BPO and Shared Services
Protect client information across teams, shifts, endpoints, facilities and subcontractors.
Fintech and Payment Platforms
Control privileged access, transaction systems, interfaces, monitoring and third-party dependencies.
Healthcare and Health Technology
Protect patient, diagnostic and operational data while managing connected systems and vendors.
Automotive Engineering Centres
Secure design files, connected-product information, supplier portals and engineering collaboration.
Data Centres and Managed Services
Coordinate physical, logical, operational and continuity controls for hosted environments.
From scope and risk assessment to an auditable ISMS
ISO 27001 implementation works best when risk treatment and operational evidence are developed together.
Define the ISMS boundary
Confirm sites, services, systems, people, interfaces and exclusions that shape the certification scope.
Establish risk methodology
Set criteria for likelihood, impact, acceptance, ownership and consistent information-security risk evaluation.
Assess and treat risks
Identify assets, threats and vulnerabilities, then select avoidance, modification, sharing or acceptance options.
Implement Annex A controls
Prepare the Statement of Applicability and operate selected organisational, people, physical and technological controls.
Measure and challenge
Monitor objectives, incidents, supplier performance, vulnerabilities and control effectiveness through internal audit.
Review and certify
Complete management review, corrective actions and evidence preparation for the certification audit stages.
Policies, registers and records expected during ISO 27001 assessment
Documentation should explain the organisation's security logic and provide evidence that selected controls are operating.
Common ISMS records
- ISMS scope and policy
- Risk assessment methodology
- Information risk register
- Risk treatment plan
- Statement of Applicability
- Asset and access records
- Supplier security assessments
- Incident response records
- Internal audit programme
- Management review minutes
ISMS mistakes that weaken assurance
Certification problems often arise when technical controls exist but governance, risk reasoning or operating evidence is incomplete.
- Copying a generic risk register that does not reflect real services and information flows.
- Selecting all Annex A controls without documenting applicability and treatment rationale.
- Restricting the ISMS to IT while business owners and suppliers remain outside the process.
- Listing policies without retaining logs, reviews, approvals or test evidence.
- Accepting residual risk informally without defined authority or review dates.
Related ISO/IEC 27001 Services for Chennai Organisations
For a connected requirement, review SOC 2 services in Chennai to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review VAPT services in Chennai where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review ISO 9001 services in Chennai to reduce duplicated work and build a coherent assurance programme.
ISO 27001 questions from Chennai-based organisations
These answers focus on risk assessment, Annex A, scope, evidence and certification.
What is an Information Security Management System?
An ISMS is a coordinated set of policies, risk processes, responsibilities, controls and reviews used to protect information and improve security performance.
Does ISO 27001 require every Annex A control?
No. The organisation considers all Annex A controls, but selects those needed based on risk treatment and other requirements, documenting decisions in the Statement of Applicability.
What is the Statement of Applicability?
It records control applicability, justification, implementation status and references, providing a bridge between risk treatment and the Annex A control set.
Can a cloud-based company be certified to ISO 27001?
Yes. The organisation must define its scope and manage shared responsibilities, suppliers, access, configuration, monitoring, backup and incident obligations.
How detailed should the information risk register be?
It should be detailed enough to support consistent decisions, clear ownership, treatment tracking and residual risk acceptance without becoming unmanageable.
Is penetration testing mandatory for ISO 27001?
The standard does not prescribe one universal test schedule, but vulnerability and security testing may be necessary based on risk, contractual duties and selected controls.
How are suppliers included in an ISMS?
Suppliers are assessed according to the information, systems and services they affect, with security requirements, monitoring and exit arrangements defined as appropriate.
What is the difference between risk assessment and risk treatment?
Assessment identifies and evaluates risk. Treatment decides what to do about it, assigns actions, selects controls and documents residual risk.
Can ISO 27001 support client security questionnaires?
Yes. A controlled ISMS provides policies, risk records, audits, incident processes and control evidence that can make due diligence more consistent.
How does Qualitcert support ISO 27001 in Chennai?
Qualitcert can help define scope, create the risk framework, prepare the Statement of Applicability, document controls, audit the ISMS and prepare for certification.
Turn Chennai Information Risks into an ISO 27001 Roadmap
Qualitcert can review your current controls, scope boundaries, risk method, Statement of Applicability and evidence model before defining the implementation sequence.