
ISO Certifications
Chen
nai
Consulting &
ISO Certifications
-ISO Certification-
QUALIT
CERT
SOC II Certification & Consulting Service in Chennai
Qualitcert, a leading certification and consulting service provider, extends its expertise to Chennai, India, offering specialized support for SOC 2 (System and Organization Controls 2) certification. SOC 2 certification demonstrates an organization’s commitment to ensuring the security, availability, processing integrity, confidentiality, and privacy of customer data. Qualitcert assists organizations in implementing robust frameworks aligned with SOC 2 standards, including comprehensive risk assessment, development of policies and procedures, and implementation of security controls. With expert guidance from Qualitcert consultants, businesses receive support in documentation, training, and system integration to establish and maintain SOC 2 compliance effectively. Qualitcert also facilitates preparation for SOC 2 audits, enabling organizations to demonstrate their adherence to stringent security and privacy requirements. Through their services, Qualitcert empowers businesses in Chennai to build trust with customers, enhance data security practices, and mitigate risks associated with handling sensitive information.
Get In Touch
Approach and Methodology used to implement Management System Standard
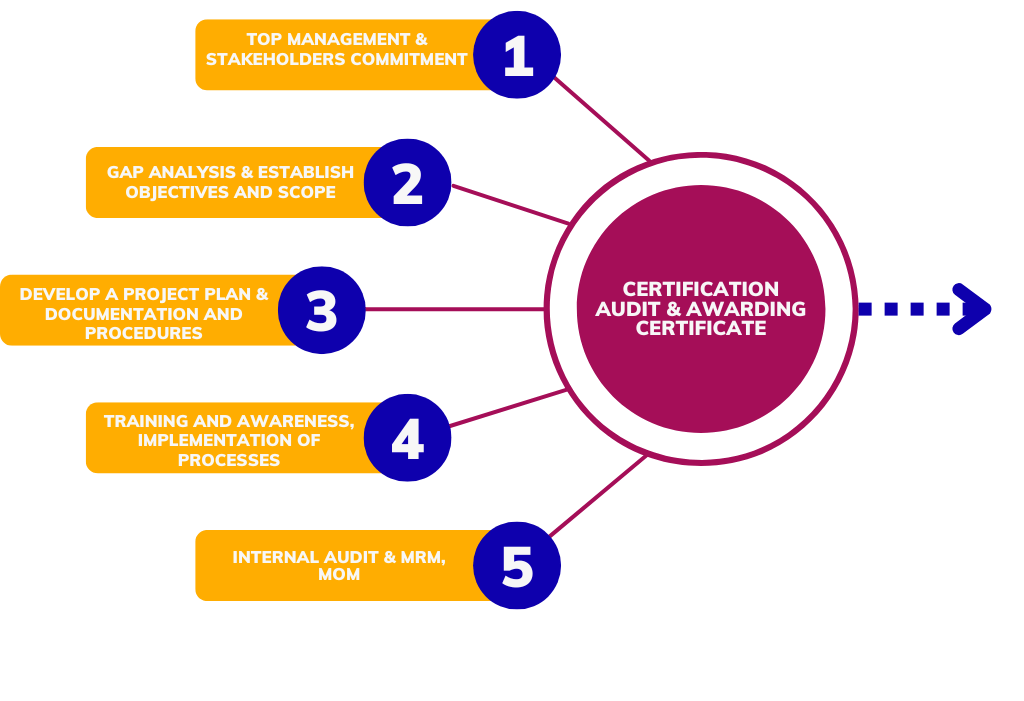
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
SOC 2 Readiness Consulting in Chennai
Prepare your service organisation for assurance against the Trust Services Criteria for security and any additional categories relevant to customer commitments.
Translate Service Commitments into Testable Controls
SOC 2 reports help service organisations communicate how controls address the Trust Services Criteria. Security is mandatory, while availability, confidentiality, processing integrity and privacy may be included when relevant.
Qualitcert helps Chennai providers define the system boundary, service commitments, principal risks, control activities and supporting evidence.
Readiness work covers governance, logical and physical access, change management, system operations, vendor management, incident response, risk assessment and monitoring.
The programme is designed for a Type I or Type II examination and aligns control descriptions with how the service actually operates.
Customer Assurance for Chennai's Digital Service Economy
SaaS, cloud, BPO, fintech and managed-service providers in Chennai are frequently asked to provide independent assurance before handling sensitive customer workloads.
Security questionnaires alone rarely give customers confidence that controls operate consistently. SOC 2 creates a structured report that explains the service and includes auditor testing.
The most effective readiness programmes start with clear service commitments and evidence ownership rather than copying a generic control catalogue.
Qualitcert helps teams select relevant criteria, close gaps and establish evidence routines before the formal examination period.
What SOC 2 readiness can achieve
The programme creates value when assurance requirements are converted into normal operating routines.
More efficient due diligence
A structured report addresses recurring customer questions with independently examined evidence.
Clearer service commitments
Security, availability and data-handling promises are linked to owned and monitored controls.
Improved operational maturity
Access, changes, incidents, suppliers and continuity activities become repeatable and measurable.
Better risk communication
Management can see control gaps, residual risks and investment priorities across the service system.
SOC 2 applications for Chennai-based providers
The appropriate criteria and controls depend on the service, data, architecture and commitments made to customers.
SaaS Product Companies
Control secure development, tenant access, deployment, monitoring, incident response and availability commitments.
Cloud and Managed Service Providers
Demonstrate infrastructure, access, change, backup, monitoring and vendor controls.
BPO and Customer Operations
Protect client data across people, facilities, applications, endpoints and subcontractors.
Fintech Platforms
Address transaction services, security, availability, confidentiality and third-party dependencies.
Data Centres and Colocation
Coordinate physical security, environmental controls, access, operations and service continuity.
Analytics and AI Service Providers
Govern data ingestion, model or platform access, change, confidentiality and processing commitments.
Build evidence around selected Trust Services Criteria
The route aligns report scope with commitments, risk and the evidence the organisation can sustain.
Define services and criteria
Confirm system boundaries, users, data, commitments and applicable Trust Services Criteria.
Assess risks and controls
Map relevant risks to controls across governance, access, change, operations, vendors and incidents.
Write the system description
Describe infrastructure, software, people, procedures, data and boundaries consistently.
Operationalise evidence
Assign owners, retain populations and standardise approvals, reviews, tests and exceptions.
Run readiness testing
Sample controls, identify gaps and verify that evidence supports the stated frequency and design.
Prepare for examination
Stabilise controls, select the reporting period and coordinate requests with the assurance practitioner.
Policies and operating records for Trust Services assurance
The evidence set should allow independent testing without relying on verbal explanations or documents created after the event.
Typical SOC 2 readiness records
- System and service description
- Risk assessment
- Trust criteria control matrix
- Information security policies
- Access approval and review records
- Change and deployment evidence
- Vulnerability and incident records
- Backup and recovery tests
- Vendor due-diligence records
- Monitoring and management review
SOC 2 preparation mistakes
Readiness suffers when scope and criteria are chosen for marketing rather than based on services and sustainable controls.
- Selecting optional criteria without relevant customer commitments.
- Using ISO policies without mapping them to SOC 2 control evidence.
- Writing a system description that omits cloud or subservice dependencies.
- Calling informal conversations evidence of approval or review.
- Beginning the Type II period before recurring controls are stable.
Related SOC 2 Services for Chennai Organisations
For a connected requirement, review ISO/IEC 27001 services in Chennai to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review VAPT services in Chennai where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review SOC 1 services in Chennai to reduce duplicated work and build a coherent assurance programme.
SOC 2 questions from Chennai service providers
These answers explain Trust Services Criteria, report types, evidence and readiness.
What are the five Trust Services Criteria categories?
They are security, availability, processing integrity, confidentiality and privacy. Security is common to every SOC 2 report.
Does every SOC 2 report include all five categories?
No. Optional categories are selected according to service commitments, risks and user needs.
What is the difference between SOC 2 Type I and Type II?
Type I evaluates design at a specified date. Type II also evaluates operating effectiveness across a defined period.
Is SOC 2 a certification?
It is an independent assurance report, not an ISO-style certification.
What is included in the SOC 2 system description?
It describes services, infrastructure, software, people, procedures, data, boundaries, commitments and relevant subservice organisations.
Can ISO 27001 controls support SOC 2?
Yes. Many controls can support both, but the evidence must be mapped to the selected Trust Services Criteria and report scope.
How should vendor risk be evidenced?
Evidence may include due diligence, contracts, security requirements, monitoring, review frequency and actions taken for identified issues.
What evidence is needed for access controls?
Typical evidence includes requests, approvals, provisioning, privileged-access review, periodic user review, removal and exception handling.
How should a company prepare for a Type II period?
It should stabilise control design, define populations, retain evidence consistently and resolve readiness findings before the period starts.
How does Qualitcert support SOC 2 readiness in Chennai?
Qualitcert can support criteria selection, control mapping, system descriptions, evidence testing, remediation and examination preparation.
Prepare Your Chennai Service Organisation for SOC 2
Qualitcert can define the system boundary, relevant Trust Services Criteria, control gaps and evidence plan for a Type I or Type II examination.