

Trust evidence for digital and outsourced services
SOC 2 reporting helps service organizations demonstrate controls relevant to the Trust Services Criteria. The most common criterion is security, while availability, processing integrity, confidentiality and privacy may be included depending on customer expectations and service commitments.
Salmiya businesses that operate SaaS platforms, booking systems, managed IT support, customer portals, healthcare support tools, outsourced administration or professional service platforms may face client due diligence questions about access, change, incident, vendor and data protection controls.
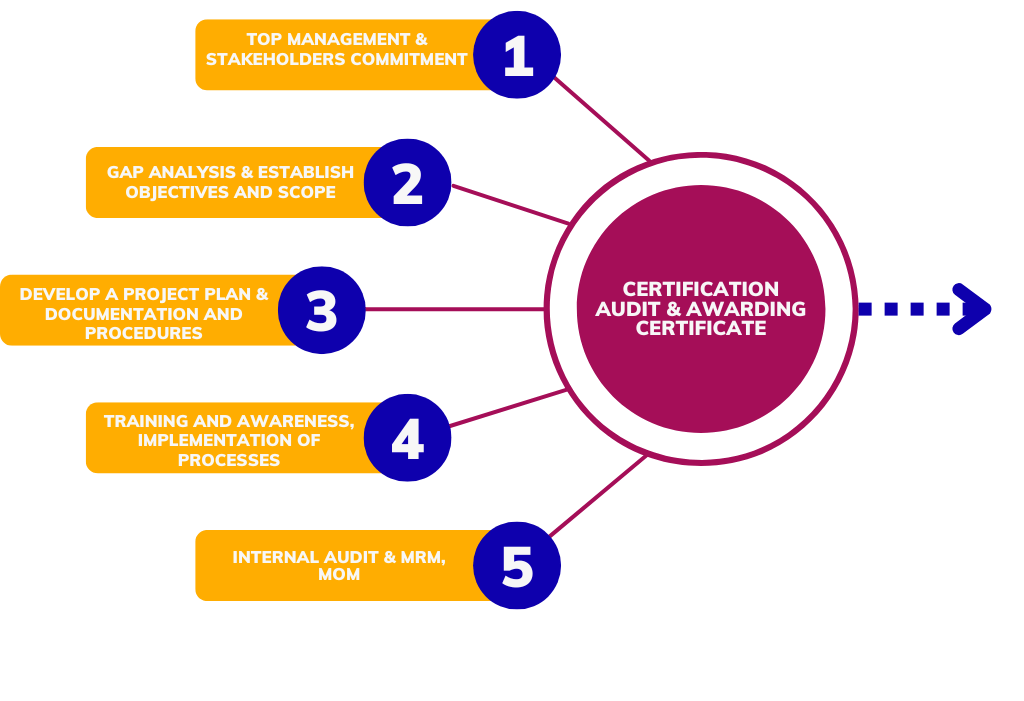
The purpose of SOC 2 readiness is to define the system, map controls, prepare policies, collect evidence, close gaps and support reporting over a defined period. SOC 2 is different from a simple cybersecurity scan because it evaluates governance and operational control evidence.
Qualitcert supports SOC 2 consulting, readiness assessment, control mapping, policy preparation, evidence planning, internal review and remediation support for Salmiya service organizations. The readiness work should make customer commitments, system boundaries, subservice organizations and evidence frequency clear before the reporting period begins.