

An ISMS for confidential data and digital service reliability
ISO 27001 is the international standard for Information Security Management Systems. It gives organizations a structured method to identify information assets, assess risks, select controls, manage incidents and continually improve information security performance.
Salmiya businesses increasingly depend on booking systems, point-of-sale applications, cloud files, customer databases, clinic records, online learning platforms, payment workflows and outsourced IT support. Weak access control or poor supplier oversight can expose confidential information and disrupt service.
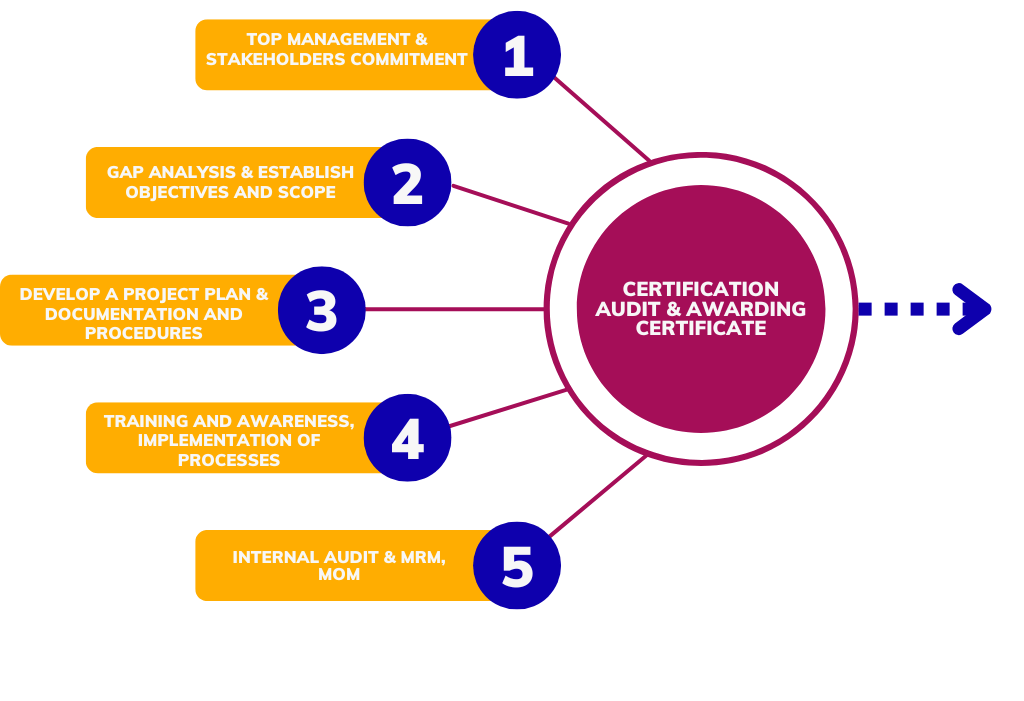
The purpose of ISO 27001 certification is to prove that information security is managed through policy, governance and evidence. This includes scope definition, asset inventory, risk assessment, risk treatment plan, Statement of Applicability, Annex A controls, internal audit and management review.
Qualitcert supports ISO 27001 consulting, gap analysis, risk assessment facilitation, documentation, control implementation guidance, internal audit preparation and certification readiness for Salmiya organizations.