Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

salmiya

Consulting &

ISO Certifications

-ISO Certification-

SOC I Certification Services in Salmiya

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

In order to assist firms in improving their operational efficiency and fortifying their internal controls, Qualitcert provides complete SOC I certification services in Salmiya. For service firms that manage financial reporting and data processing, this certification which is based on the Statement on Standards for Attestation Engagements (SSAE) 18 is essential. The knowledgeable staff at Qualitcert helps clients with every step of the certification process, from the first evaluation and gap analysis to the final audit and the installation of required controls. Organizations may reassure clients and stakeholders about the integrity of their financial processes and data management procedures by obtaining SOC I accreditation, which shows their dedication to upholding high security and reliability standards.

Get In Touch

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

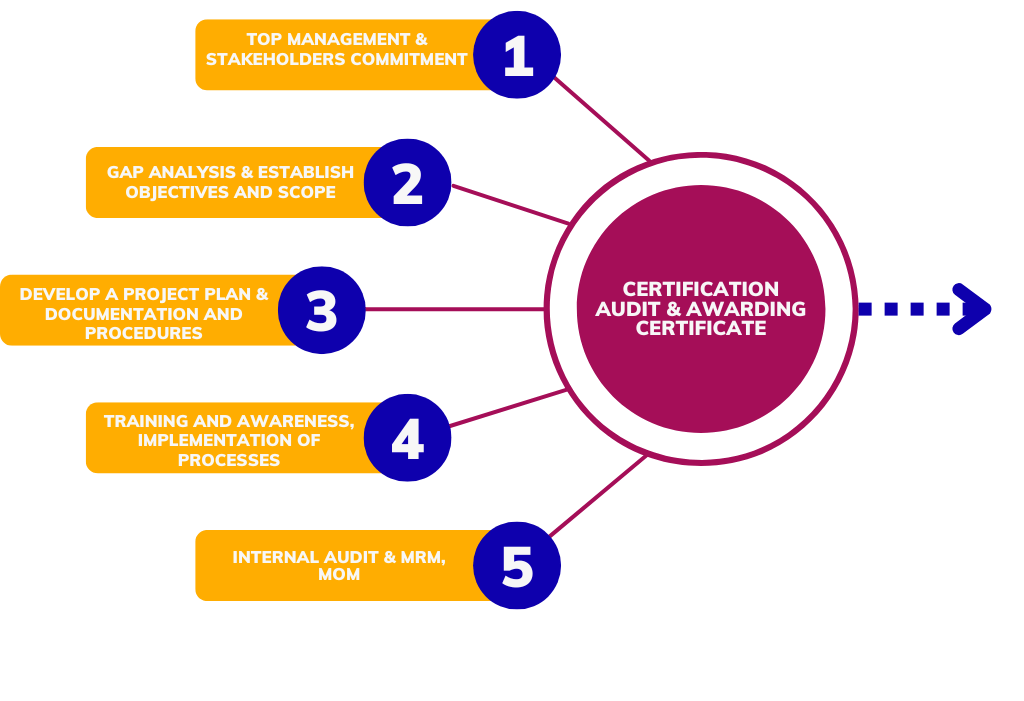
Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO  standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
Financial Control Reporting for Salmiya

SOC 1 Certification Services in Salmiya for Internal Controls over Financial Reporting

SOC 1 focuses on internal controls at a service organization that may affect user entities’ financial reporting, including transaction processing, reconciliations, authorization and control monitoring.

Control assurance for financial reporting dependencies

SOC 1 reporting is designed for service organizations whose services can affect a client’s internal controls over financial reporting. It is often relevant where a provider processes transactions, manages financial data, performs billing activities or supports systems used in financial reporting.

In Salmiya, professional service firms, payroll processors, accounting support providers, hosted software operators, payment support teams, administrative outsourcing firms and property service organizations may be asked by clients to demonstrate financial control assurance.

The purpose of SOC 1 readiness is to prepare a clear system description, define control objectives, document control activities, collect evidence and resolve gaps before the reporting engagement. It is different from ISO certification because SOC 1 is an assurance report focused on ICFR-related controls.

Qualitcert supports SOC 1 consulting, gap assessment, control mapping, evidence preparation, internal readiness review and management support for Salmiya service organizations. Readiness should also define which controls are performed by the service organization, which are expected from clients and how complementary user-entity controls are described.

ICFR Service Context

Demonstrating Controls That Affect Client Financial Reporting

For Salmiya service providers, SOC 1 readiness is relevant when clients depend on outsourced processes that feed accounting, billing, payroll, payment, claims or financial records.

Salmiya service providers may support client billing, account administration, subscription management, property collections, payroll data, payment files or financial system workflows. If those processes affect client financial reporting, clients may request control assurance.

SOC 1 certification services in Salmiya help organizations prepare for that request by identifying which processes are in scope, what control objectives apply and what evidence is needed. This can include approvals, reconciliations, access reviews, change records, exception reports and management reviews.

The readiness work should not blur SOC 1 with SOC 2. SOC 1 is about controls relevant to financial reporting, while SOC 2 focuses on Trust Services Criteria such as security, availability, processing integrity, confidentiality and privacy.

Control Assurance

SOC 1 Benefits for Salmiya Service Organizations

The report helps clients and their auditors understand control design and operating effectiveness without repeating unnecessary control testing.

Client audit support

SOC 1 evidence can reduce repeated control questions from clients and their auditors.

Clearer control ownership

Control objectives, activities, evidence owners and review responsibilities become defined.

Improved exception management

Exceptions can be tracked, analyzed and remediated before they affect reporting confidence.

Stronger service credibility

A prepared control environment supports trust for financially significant outsourced services.

Where SOC 1 Applies

Industry Applications for SOC 1 in Salmiya

SOC 1 is suitable for service organizations whose activities can influence client financial statements or internal controls over financial reporting.

01

Payroll and HR processing

Demonstrate controls over payroll input, authorization, calculation review and reporting files.

02

Accounting support services

Control journal support, reconciliations, document handling and client financial data workflows.

03

Property management services

Manage rent collections, service charge records, approvals, adjustments and reporting controls.

04

SaaS platforms for finance

Show access, change management, processing and reporting controls that support client accounting.

05

Payment support providers

Control transaction files, approvals, settlement support, exceptions and reconciliation records.

06

Administrative outsourcing

Demonstrate controlled handling of client records that influence financial reporting.

SOC 1 Readiness Path

A Practical SOC 1 Readiness Journey

Readiness should define the system, control objectives, control activities, evidence, exceptions and management responsibilities.

01

Define SOC 1 scope

Confirm services, systems, locations, processes and financial reporting dependencies included.

02

Map control objectives

Identify what the controls need to achieve for user entities and their auditors.

03

Document activities

Describe approvals, reconciliations, access controls, change controls and exception handling.

04

Collect evidence

Gather control samples, logs, review records, approvals and management sign-offs.

05

Run readiness review

Check whether controls are designed, operating and documented consistently.

06

Support reporting

Resolve gaps, prepare management representation and coordinate the assurance engagement.

SOC 1 Evidence

Control Descriptions, Testing Evidence and Reporting Records

Evidence should show that controls are designed properly and operated consistently over the reporting period.

Typical SOC 1 Records

  • System description
  • Control objective matrix
  • Process flow narrative
  • Access review record
  • Approval evidence
  • Reconciliation record
  • Change log
  • Exception report
  • Management review record
  • Remediation tracker
SOC 1 evidence should be retained consistently across the reporting period, not assembled only at the end.

Common SOC 1 Readiness Mistakes

These issues often create gaps in SOC 1 readiness reviews.

  • Including processes that do not affect financial reporting.
  • Using broad control statements without testable evidence.
  • Missing review signatures, timestamps or exception follow-up.
  • Confusing cybersecurity controls with ICFR control objectives.
  • Waiting until the reporting period ends to collect evidence.
SOC 1 readiness works best when control owners understand why each activity matters to client financial reporting.
Related Salmiya Services

For aligned planning, review SOC 2 certification services in Salmiya when clients also require assurance over security, availability, confidentiality or privacy controls.

When the same teams own connected controls, compare ISO 27001 certification services in Salmiya when information security governance supports systems used in financial reporting.

For wider readiness work, consider VAPT certification company in Salmiya when technical testing is needed to support cybersecurity remediation outside the SOC 1 financial reporting scope.

FAQs

SOC 1 Questions from Salmiya Service Providers

These FAQs explain SOC 1 purpose, scope and readiness.

What is SOC 1 reporting?

SOC 1 reporting evaluates controls at a service organization that are relevant to user entities’ internal controls over financial reporting.

Who needs SOC 1 in Salmiya?

Service organizations that process financial data, payroll, billing, transactions, reconciliations or systems that affect client financial reporting may need SOC 1.

How is SOC 1 different from SOC 2?

SOC 1 focuses on financial reporting controls, while SOC 2 focuses on Trust Services Criteria such as security, availability, processing integrity, confidentiality and privacy.

What is the difference between Type 1 and Type 2?

Type 1 reports on control design at a point in time, while Type 2 reports on design and operating effectiveness over a period.

What evidence is needed for SOC 1?

Evidence may include approvals, reconciliations, access reviews, change records, exception reports, control logs and management review records.

What is a system description?

A system description explains the services, processes, systems, people, controls and boundaries included in the SOC 1 report.

Can ISO 27001 replace SOC 1?

No. ISO 27001 supports information security management, while SOC 1 addresses controls relevant to client financial reporting.

What are control objectives?

Control objectives define what the control activities are intended to achieve for user entities and their auditors.

How can a company prepare for SOC 1?

Preparation includes scope definition, control mapping, evidence collection, gap remediation and readiness review.

How does Qualitcert support SOC 1 in Salmiya?

Qualitcert supports SOC 1 readiness, control documentation, evidence planning, gap review and preparation for assurance reporting.

Speak with Qualitcert

Prepare SOC 1 Readiness in Salmiya

Share your service scope, client control requests and financial reporting workflows. Qualitcert can help prepare SOC 1 readiness for your Salmiya service organization.

Request SOC 1 Consultation →
Scroll to Top