
ISO Certifications
Philippines
Consulting &
ISO Certifications
-ISO Certification-
QUALIT
CERT
SOC II Certification & Consulting Service in Philippines
Qualitcert is the premier provider of SOC 2 certification and consulting services in the Philippines, specializing in assisting organizations in demonstrating their commitment to information security and privacy. With a comprehensive understanding of SOC 2 requirements and their significance in ensuring the integrity, confidentiality, and availability of data, Qualitcert delivers tailored consulting services aimed at facilitating the certification process seamlessly. Their approach includes thorough assessments, gap analysis, development of information security policies and controls, documentation support, and strategic guidance to ensure alignment with SOC 2 criteria. From implementing security measures to conducting risk assessments and providing staff training, Qualitcert empowers organizations to achieve SOC 2 certification effortlessly. Renowned for their expertise, reliability, and commitment to excellence, Qualitcert serves as the trusted partner for Filipino businesses seeking SOC 2 certification and demonstrating their commitment to protecting sensitive information and maintaining customer trust.
Get In Touch
Approach and Methodology used to implement Management System Standard
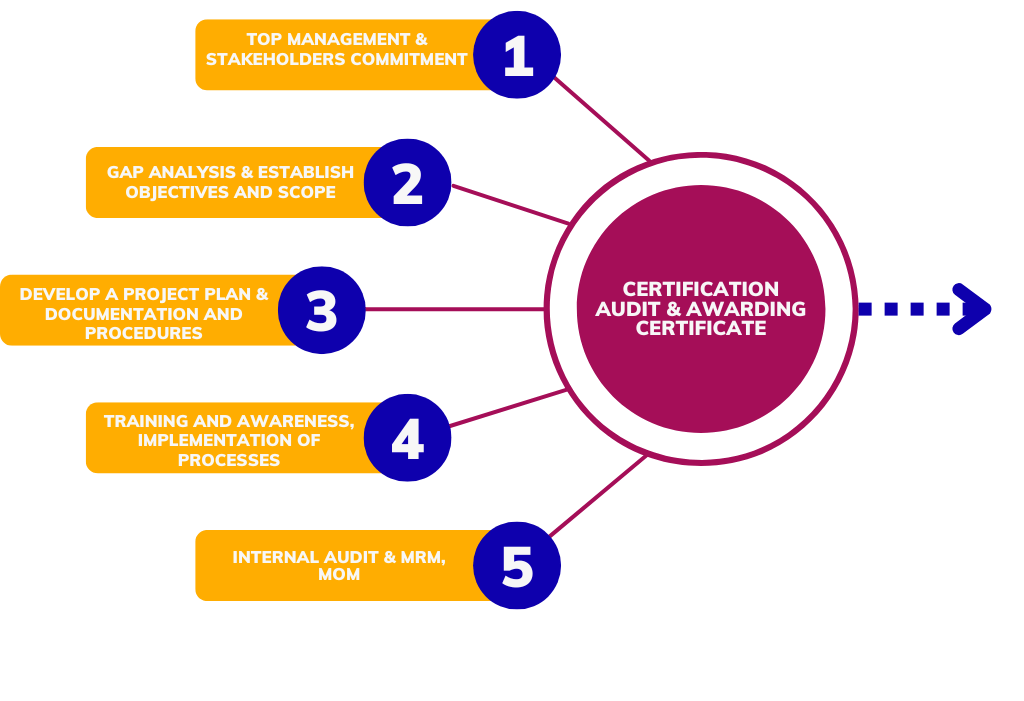
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
SOC 2 Services in the Philippines for Secure and Reliable Service Organisations
SOC 2 helps Philippine technology and outsourced-service providers demonstrate controls against the Trust Services Criteria.
Translate service commitments into testable controls
A SOC 2 examination evaluates controls using the AICPA Trust Services Criteria. Security is always included, while availability, confidentiality, processing integrity and privacy are selected as relevant.
Software, BPO, fintech, managed-service and cloud providers in the Philippines increasingly answer customer assurance requests covering security, resilience and information handling.
Scoping requires a system description covering infrastructure, software, people, procedures and data. Risks and controls are mapped to governance, access, changes, incidents, vendors and continuity.
Qualitcert supports criteria selection, readiness assessment, policy design, control ownership, evidence calendars and preparation for Type I or Type II examination.
Customer trust for the Philippines' technology-enabled service economy
Enterprise customers expect evidence that providers protect information, maintain service commitments and respond effectively to control failures.
Identity management, configuration, vulnerability handling, logging and code changes require defined ownership and retained evidence.
Availability commitments may require capacity planning, backup, recovery tests and incident communication. Confidentiality and privacy add classification and retention controls.
Type II readiness depends on sustained operation, so teams need evidence schedules, exception review and accountable control owners.
What SOC 2 readiness can achieve
The programme creates value when assurance requirements are converted into normal operating routines.
More efficient due diligence
A structured report addresses recurring customer questions with independently examined evidence.
Clearer service commitments
Security, availability and data-handling promises are linked to owned and monitored controls.
Improved operational maturity
Access, changes, incidents, suppliers and continuity activities become repeatable and measurable.
Better risk communication
Management can see control gaps, residual risks and investment priorities across the service system.
SOC 2 applications for Philippinea-based providers
The appropriate criteria and controls depend on the service, data, architecture and commitments made to customers.
Software-as-a-service providers
Evidence secure development, access, monitoring, change approval and data protection.
BPO and shared services
Control workforce access, confidentiality, service delivery and continuity.
Fintech and payment platforms
Coordinate security, availability, processing, vendor risk and incidents.
Managed IT services
Demonstrate administrative access, configuration, monitoring, changes and backups.
Cloud and hosting providers
Manage infrastructure, customer responsibilities, resilience and incident response.
Digital commerce platforms
Control customer data, availability, payment dependencies and system changes.
Build evidence around selected Trust Services Criteria
The route aligns report scope with commitments, risk and the evidence the organisation can sustain.
Define services and criteria
Confirm system boundaries, users, data, commitments and applicable Trust Services Criteria.
Assess risks and controls
Map relevant risks to controls across governance, access, change, operations, vendors and incidents.
Write the system description
Describe infrastructure, software, people, procedures, data and boundaries consistently.
Operationalise evidence
Assign owners, retain populations and standardise approvals, reviews, tests and exceptions.
Run readiness testing
Sample controls, identify gaps and verify that evidence supports the stated frequency and design.
Prepare for examination
Stabilise controls, select the reporting period and coordinate requests with the assurance practitioner.
Policies and operating records for Trust Services assurance
The evidence set should allow independent testing without relying on verbal explanations or documents created after the event.
Typical SOC 2 readiness records
- System and service description
- Risk assessment
- Trust criteria control matrix
- Information security policies
- Access approval and review records
- Change and deployment evidence
- Vulnerability and incident records
- Backup and recovery tests
- Vendor due-diligence records
- Monitoring and management review
SOC 2 preparation mistakes
Readiness suffers when scope and criteria are chosen for marketing rather than based on services and sustainable controls.
- Selecting optional criteria without relevant customer commitments.
- Using ISO policies without mapping them to SOC 2 control evidence.
- Writing a system description that omits cloud or subservice dependencies.
- Calling informal conversations evidence of approval or review.
- Beginning the Type II period before recurring controls are stable.
Related SOC 2 Services for Philippine Organisations
For a connected requirement, review ISO/IEC 27001 services in the Philippines to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review VAPT services in the Philippines where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review SOC 1 services in the Philippines to reduce duplicated work and build a coherent assurance programme.
SOC 2 questions from Philippine service providers
These answers explain Trust Services Criteria, report types, evidence and readiness.
What are the five Trust Services Criteria categories?
They are security, availability, processing integrity, confidentiality and privacy. Security is common to every SOC 2 report.
Does every SOC 2 report include all five categories?
No. Optional categories are selected according to service commitments, risks and user needs.
What is the difference between SOC 2 Type I and Type II?
Type I evaluates design at a specified date. Type II also evaluates operating effectiveness across a defined period.
Is SOC 2 a certification?
It is an independent assurance report, not an ISO-style certification.
What is included in the SOC 2 system description?
It describes services, infrastructure, software, people, procedures, data, boundaries, commitments and relevant subservice organisations.
Can ISO 27001 controls support SOC 2?
Yes. Many controls can support both, but the evidence must be mapped to the selected Trust Services Criteria and report scope.
How should vendor risk be evidenced?
Evidence may include due diligence, contracts, security requirements, monitoring, review frequency and actions taken for identified issues.
What evidence is needed for access controls?
Typical evidence includes requests, approvals, provisioning, privileged-access review, periodic user review, removal and exception handling.
How should a company prepare for a Type II period?
It should stabilise control design, define populations, retain evidence consistently and resolve readiness findings before the period starts.
How does Qualitcert support SOC 2 readiness in Philippinea?
Qualitcert can support criteria selection, control mapping, system descriptions, evidence testing, remediation and examination preparation.
Prepare Your Philippine Service Organisation for SOC 2
Share your architecture, customer commitments and controls. Qualitcert can help structure a practical Trust Services Criteria readiness programme.