
ISO Certifications
Philippines
Consulting &
ISO Certifications
-ISO Certification-
QUALIT
CERT
SOC I Certification & Consulting Service in Philippines
Qualitcert stands as the premier provider of SOC 1 certification and consulting services in the Philippines, specializing in assisting organizations in demonstrating their commitment to internal controls and financial reporting. With a comprehensive understanding of SOC 1 requirements and their significance in ensuring the reliability of financial statements, Qualitcert delivers tailored consulting services aimed at facilitating the certification process seamlessly. Their approach encompasses comprehensive assessments, gap analysis, development of control frameworks, documentation support, and strategic guidance to ensure alignment with SOC 1 criteria. From implementing control measures to conducting audits and providing staff training, Qualitcert empowers organizations to achieve SOC 1 certification effortlessly. Renowned for their expertise, reliability, and commitment to excellence, Qualitcert serves as the trusted partner for Filipino businesses seeking SOC 1 certification and demonstrating their dedication to financial integrity and accountability.
Get In Touch
Approach and Methodology used to implement Management System Standard
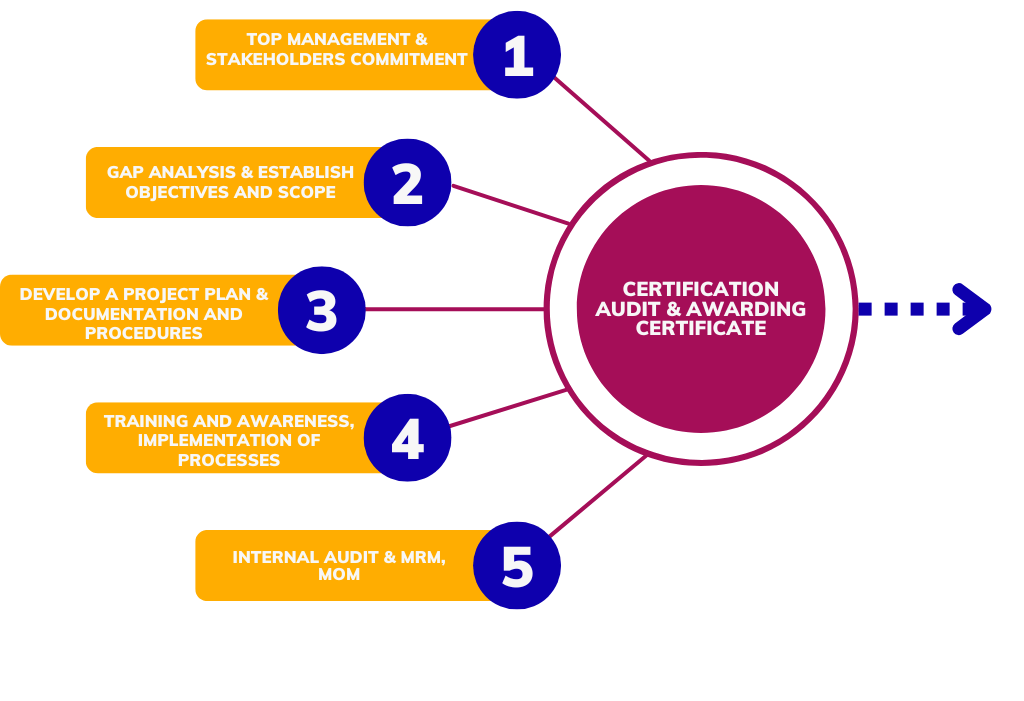
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
SOC 1 Services in the Philippines for Controls Affecting Financial Reporting
SOC 1 helps Philippine service organisations demonstrate controls relevant to customers' internal control over financial reporting.
Define the outsourced controls that influence the financial close
A SOC 1 examination addresses controls at a service organisation that are relevant to user entities' internal control over financial reporting.
Payroll processors, payment services, finance BPO providers, billing platforms and hosted financial systems in the Philippines may process data that enters customer ledgers or disclosures.
Readiness begins by defining the service, system boundaries, control objectives, subservice organisations and complementary user-entity controls.
Qualitcert supports scope workshops, risk-control mapping, evidence design, walkthroughs, remediation and readiness assessment before independent attestation.
Assurance for Philippine outsourced processes entering financial reporting
Customers need evidence that transaction integrity, access, changes, interfaces and reconciliations operate consistently.
Business-process controls may cover input validation, authorisation, exception handling, reconciliations, interfaces and output review.
Technology general controls support these objectives through user provisioning, privileged access, program changes, job monitoring, backup and incident handling.
A Type I report evaluates control design at a point in time, while a Type II report also tests operating effectiveness over a defined period.
Why service organisations pursue SOC 1 readiness
The report can reduce repeated customer audit effort when the service genuinely affects financial-reporting controls.
Clearer customer assurance
A structured report explains relevant controls and testing to user entities and their auditors.
Better control accountability
Owners, frequencies, evidence and exception criteria are defined for financially relevant activities.
Reduced audit disruption
Reusable assurance evidence can replace multiple overlapping customer control reviews.
Stronger process discipline
Reconciliations, approvals, access and change controls become more consistent and reviewable.
Philippine service scenarios where SOC 1 may be relevant
SOC 1 applies when the outsourced service can materially influence a customer's financial statements or ICFR.
Payroll and HR service providers
Control authorised inputs, calculations, changes, payment files and reconciliation.
Accounting and finance BPO
Standardise journal support, approvals, close tasks, interfaces and reconciliations.
Payment and remittance services
Demonstrate transaction completeness, settlement, access and exception handling.
Billing and subscription platforms
Control source data, rate changes, invoice generation, exceptions and interfaces.
Financial-system hosting
Evidence access, change control, processing, backup and incident controls.
Loan and claims administrators
Manage authorised data, calculations, disbursements, reconciliations and outputs.
From ICFR impact analysis to examination-ready evidence
The preparation route begins with the service's financial-reporting effect and ends with sustainable control operation.
Confirm report users and scope
Define services, systems, locations, subservice organisations and intended user entities.
Map ICFR-related risks
Identify how errors or unauthorised activity could affect transaction and reporting assertions.
Define objectives and controls
Document control purpose, owner, frequency, evidence, population and exception handling.
Prepare the system description
Describe services, infrastructure, people, procedures, data and control boundaries accurately.
Operate and test readiness
Collect evidence, sample controls, resolve gaps and confirm complementary user entity controls.
Support the examination
Coordinate management assertion, requests, exceptions and remediation with the assurance practitioner.
Records needed for financial-control assurance readiness
Evidence should be complete enough for an examiner to identify the control population, select samples and verify operation.
Typical SOC 1 readiness evidence
- Service and system scope
- ICFR risk and control matrix
- System description
- Control owner register
- Transaction processing logs
- Approval and reconciliation records
- Access review evidence
- Change management records
- Exception and incident records
- Management assertion support
SOC 1 readiness errors
Organisations lose time when the control description is broader than the available evidence or the report is used for the wrong assurance purpose.
- Treating SOC 1 as a general cybersecurity report.
- Including controls that do not affect user-entity financial reporting.
- Describing reviews without documenting criteria and follow-up.
- Ignoring complementary user entity and subservice-organisation controls.
- Starting a Type II period before controls operate consistently.
Related SOC 1 Services for Philippine Organisations
For a connected requirement, review SOC 2 services in the Philippines to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review ISO/IEC 27001 services in the Philippines where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review ISO 9001 services in the Philippines to reduce duplicated work and build a coherent assurance programme.
SOC 1 questions from service organisations in Philippinea
These answers cover ICFR relevance, Type I and Type II reports, controls and user responsibilities.
What is a SOC 1 report used for?
It provides assurance over controls at a service organisation that are relevant to user entities' internal control over financial reporting.
Who typically requests SOC 1 assurance?
Customers whose financial reporting depends on the outsourced service, as well as their finance teams and external auditors, commonly request it.
What is the difference between SOC 1 Type I and Type II?
Type I addresses control design at a specified date, while Type II also tests operating effectiveness over a defined review period.
Is SOC 1 a certification?
SOC 1 is an independent assurance report rather than an ISO-style management-system certificate.
What are complementary user entity controls?
They are controls that customers must operate for the service organisation's controls and objectives to work as intended.
Can cybersecurity controls appear in SOC 1?
Yes, but only where they are relevant to financial-reporting risk, such as access or change controls over financially significant systems.
What should a system description include?
It should describe the service, infrastructure, software, people, procedures, data, boundaries, control objectives and relevant subservice organisations.
How long is a SOC 1 Type II review period?
The period is agreed for the engagement and should be long enough to provide meaningful operating-effectiveness evidence.
What happens when a control exception is found?
The examiner evaluates the nature and impact. Management should understand the cause, affected population, compensating controls and corrective action.
How can Qualitcert support SOC 1 readiness in Philippinea?
Qualitcert can help with scope, risk-control mapping, system descriptions, evidence preparation, readiness testing and remediation planning.
Define a SOC 1 Readiness Programme for Your Philippine Service
Share your service description, customer commitments, process flows and controls. Qualitcert can help establish a defensible SOC 1 scope.