
ISO Certifications
Philippines
Consulting &
ISO Certifications
-ISO Certification-
QUALIT
CERT
VAPT Certification & Consulting Company in Philippines
Qualitcert is the premier VAPT (Vulnerability Assessment and Penetration Testing) certification and consulting company in the Philippines, renowned for its expertise in cybersecurity assessment and mitigation strategies. Specializing in helping organizations enhance their cybersecurity posture, Qualitcert offers comprehensive VAPT services tailored to meet the unique needs of each client. Their team of cybersecurity experts conducts thorough vulnerability assessments and penetration tests to identify weaknesses in networks, systems, and applications, enabling organizations to proactively address security vulnerabilities and prevent potential cyber threats. With a customer-centric approach and commitment to excellence, Qualitcert empowers businesses to achieve VAPT certification and strengthen their defenses against cybersecurity risks. Renowned for its reliability and effectiveness, Qualitcert serves as the trusted partner for organizations in the Philippines seeking to safeguard their digital assets and protect against cyber threats.
Get In Touch
Approach and Methodology used to implement Management System Standard
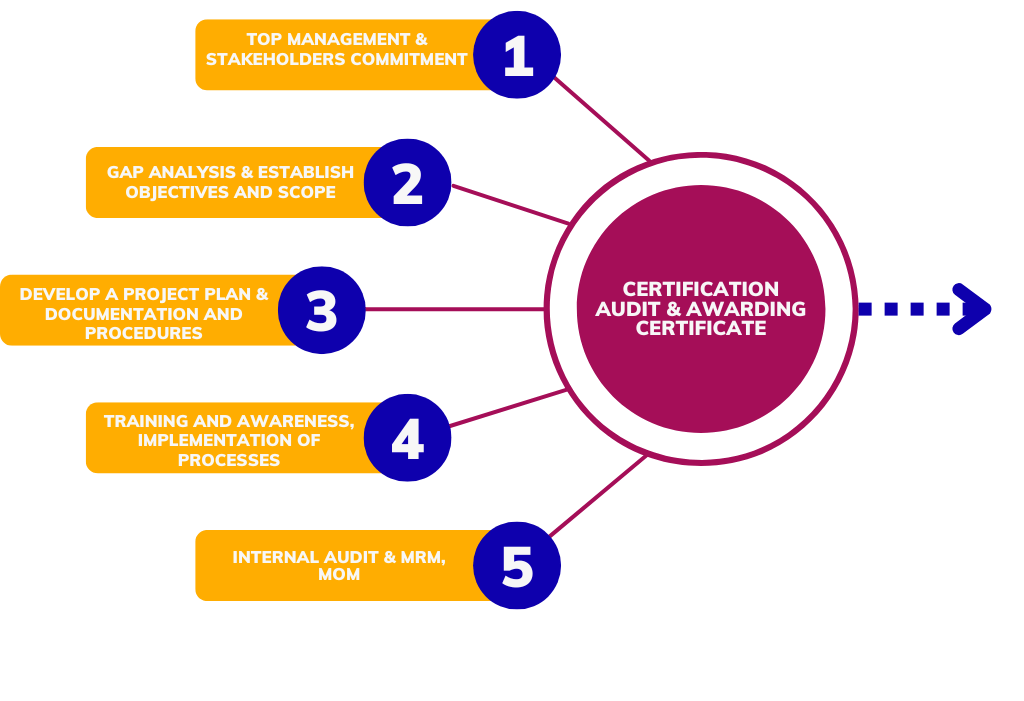
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
VAPT Services in the Philippines for Verified Vulnerabilities and Attack Paths
VAPT combines systematic vulnerability assessment with controlled penetration testing to reveal exploitable weaknesses and prioritise remediation.
Move from automated findings to validated attack paths
Vulnerability assessment identifies weaknesses across defined assets, while penetration testing safely attempts exploitation to confirm attack paths and business impact.
Organisations in the Philippines expose websites, APIs, mobile applications, remote-access gateways, cloud services and internal systems to different threat scenarios.
A controlled engagement defines scope, test windows, permitted techniques, excluded systems, data-handling rules, contacts and stopping conditions.
Qualitcert supports external, internal, web, API, mobile and cloud testing followed by risk-ranked reporting, remediation guidance and retesting.
Testing attack paths across Philippine digital services
Mobile banking, e-commerce, BPO access, public portals and third-party integrations can create exposures that configuration reviews do not reveal.
Authentication and authorisation require focused testing because weak sessions, password recovery and excessive privileges can expose sensitive data.
APIs and mobile back ends should be assessed for token handling, rate limits, input validation, data exposure and transaction logic.
Findings should identify affected assets, reproduction steps, likely impact, root conditions and recommended fixes, followed by retesting.
What disciplined VAPT provides
The value comes from validated findings and clear remediation priorities rather than raw vulnerability counts.
Verified technical risk
Manual testing separates exploitable issues from false positives and low-value scanner noise.
Prioritised remediation
Severity, exposure, exploitability and business impact guide practical action sequencing.
Stronger customer assurance
Reports and retest evidence support due diligence, compliance and contractual security expectations.
Improved engineering feedback
Root causes and attack paths help development and infrastructure teams prevent recurrence.
VAPT applications for organisations in Philippinea
The testing method should match the asset type, threat model, authentication level and operational sensitivity.
Banks and fintech
Test customer applications, payment APIs, portals and internal attack paths.
BPO and shared-service centres
Assess remote access, workforce endpoints, client platforms and segmentation.
E-commerce and digital platforms
Examine account takeover, checkout logic, API authorisation and data exposure.
Telecommunications
Assess subscriber systems, exposed services, remote access and infrastructure.
Healthcare organisations
Test patient systems, remote access and sensitive applications.
Cloud and software providers
Assess applications, infrastructure, identity, APIs and deployment controls.
A controlled route from scope to retest
The engagement protects operational stability while producing reproducible and decision-ready evidence.
Authorise and scope
Define assets, dates, methods, credentials, exclusions, contacts, data handling and stop conditions.
Discover the attack surface
Identify reachable hosts, services, applications, APIs, versions and exposed functionality.
Assess vulnerabilities
Use appropriate tools and manual analysis to identify configuration, code and control weaknesses.
Validate exploitation safely
Confirm material findings and attack paths without exceeding agreed operational limits.
Report and remediate
Document evidence, impact, severity, root cause and prioritised corrective recommendations.
Retest closed findings
Verify remediation, identify residual exposure and issue updated status evidence.
Technical records expected from a professional engagement
Deliverables should be suitable for executives, risk owners and technical teams without exposing unnecessary sensitive detail.
Typical VAPT documentation
- Signed rules of engagement
- Authorised asset list
- Testing methodology
- Credential and access plan
- Finding evidence
- Risk and severity rationale
- Executive summary
- Technical remediation guidance
- Finding owner tracker
- Retest confirmation report
Security testing mistakes
Poorly planned testing can produce misleading results or unnecessary operational risk.
- Running scans without written authorisation and scope boundaries.
- Calling automated scanning a full penetration test.
- Testing only IP addresses while ignoring applications and APIs.
- Ranking findings by scanner score without business context.
- Closing findings from screenshots without a controlled retest.
Related VAPT Services for Philippine Organisations
For a connected requirement, review ISO/IEC 27001 services in the Philippines to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review SOC 2 services in the Philippines where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review ISO 9001 services in the Philippines to reduce duplicated work and build a coherent assurance programme.
VAPT questions from organisations in Philippinea
These answers explain scope, scanning, penetration testing, reporting and remediation.
What is the difference between vulnerability assessment and penetration testing?
Vulnerability assessment identifies potential weaknesses, while penetration testing manually validates exploitability and attack impact within authorised limits.
Is an automated scan enough for VAPT?
No. Automated tools are useful, but professional testing includes manual verification, logic testing, attack-path analysis and false-positive review.
What systems can be included in VAPT?
Scope may include external or internal networks, web applications, APIs, mobile apps, cloud environments and wireless systems.
Is VAPT safe for production systems?
It can be performed safely with agreed methods, timing, stop conditions and exclusions, but residual operational risk must be assessed before testing.
What is authenticated vulnerability testing?
It uses approved credentials to inspect patching, configurations and privileges that cannot be assessed accurately from an unauthenticated position.
How are vulnerabilities prioritised?
Priority should consider technical severity, exposure, exploitability, affected data or service, compensating controls and business impact.
What should a penetration-test report contain?
It should include scope, methodology, executive findings, technical evidence, risk rationale, remediation guidance and limitations.
Why is retesting important?
Retesting confirms that the specific weakness and related attack path were removed rather than relying only on implementation statements.
How often should VAPT be performed?
Frequency should reflect risk, system change, contractual obligations and threat exposure. Major changes can trigger testing outside the routine cycle.
How does Qualitcert support VAPT in Philippinea?
Qualitcert can help define scope, coordinate testing, present prioritised findings, support remediation tracking and verify closure through retesting.
Define a Controlled VAPT Scope for Your Philippine Systems
Share your asset list, architecture and testing constraints. Qualitcert can help plan testing, prioritise findings and verify remediation.