Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

turkey

Consulting &

ISO Certifications

-ISO Certification-

SOC II Certification Consulting Services in Turkey

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

In order to help companies improve operational transparency and fortify their commitment to data security and privacy, Qualitcert provides full SOC II certification consulting services in Turkey. Qualitcert helps companies through the whole certification process, from first evaluations to the installation of required controls and continuous monitoring, thanks to a team of knowledgeable professionals. In-depth gap analysis to find gaps in current procedures, customized suggestions for enhancing security measures, and staff training on data protection best practices are all included in the consulting services. In order to ensure that companies not only achieve SOC II compliance but also develop trust with their customers and stakeholders, Qualitcert highlights the significance of aligning with the AICPA’s Trust Services Criteria. Organizations can eventually show their commitment to protecting sensitive information by utilizing Qualitcert’s expertise.

Get In Touch

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

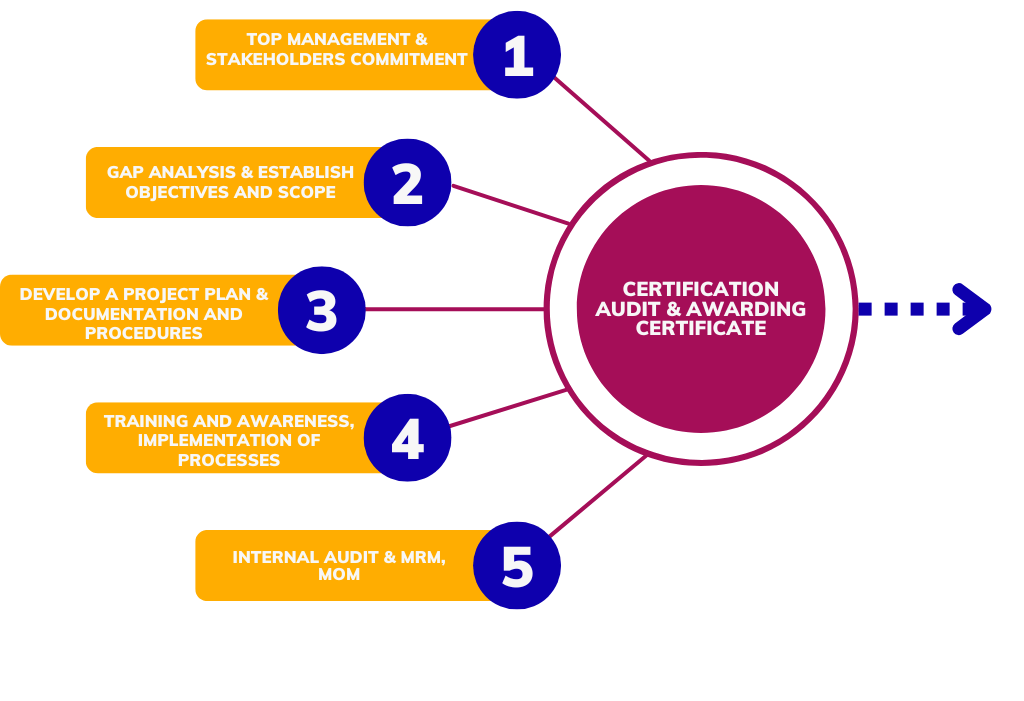
Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
Trust Services Criteria Readiness

SOC 2 Certification Consulting Services in Turkey for Service Organisation Trust Controls

SOC 2 helps Turkey service organisations demonstrate controls over security, availability, confidentiality, processing integrity or privacy using the Trust Services Criteria.

Assurance for technology and service trust

SOC 2 consulting services in Turkey focus on controls that matter to customers who rely on cloud platforms, SaaS providers, managed services, data processors, outsourcing providers or technology-enabled service companies.

Unlike SOC 1, SOC 2 is not centred on financial reporting. It evaluates controls against Trust Services Criteria, usually beginning with security and then adding availability, confidentiality, processing integrity or privacy where relevant.

Qualitcert supports readiness through scope definition, control mapping, policy preparation, evidence planning, vendor risk controls, incident response documentation and readiness testing.

A useful SOC 2 programme gives management a clear way to prove that trust commitments are supported by operating controls and retained evidence.

Turkey Context

SOC 2 Demand in Turkey's Service Economy

Turkey technology, outsourcing, fintech, healthcare technology, logistics platforms and SaaS providers often face customer security questionnaires and vendor assurance demands.

Enterprise customers need evidence that service providers manage access, change, incidents, monitoring, backup, vendors and data protection consistently.

SOC 2 readiness helps organisations convert security practices into a control framework that can be reviewed and tested by an independent auditor.

For fast-growing service companies, the discipline also supports sales cycles by reducing repeated responses to customer due diligence requests.

Operational Value

SOC 2 Benefits for Turkey Service Organisations

SOC 2 supports trust, due diligence and operational discipline.

Customer assurance

A SOC 2 report can support enterprise security and vendor reviews.

Stronger control ownership

Policies and evidence are assigned to accountable teams.

Improved security governance

Access, change, incidents and monitoring become easier to evidence.

Scalable trust programme

Controls can support growth, new customers and additional criteria.

Industry Applications

SOC 2 Applications in Turkey

SOC 2 is useful for organisations that provide systems or services customers depend on.

01

SaaS providers

Application security, availability, change management and customer data protection.

02

Managed IT services

Monitoring, access control, incident response and customer environment support.

03

Fintech platforms

Security, processing integrity, availability and vendor oversight.

04

Healthcare technology

Confidentiality, privacy-related controls and system availability.

05

E-commerce platforms

Transaction processing, user access, change control and incident response.

06

Data analytics providers

Confidentiality commitments, data handling and secure processing controls.

Certification Journey

SOC 2 Readiness and Reporting Route

The journey is built around criteria selection, control design and evidence collection.

01

Confirm scope and criteria

Select services, systems, boundaries and Trust Services Criteria.

02

Map controls

Link commitments, risks and criteria to control activities.

03

Prepare policies

Document security, access, change, vendor, incident and data procedures.

04

Collect evidence

Operate controls and retain evidence over the readiness period.

05

Test gaps

Review control design and sample operating evidence.

06

Support audit

Prepare management assertion and evidence for the SOC auditor.

Documentation and Evidence

SOC 2 Documentation and Control Evidence

SOC 2 evidence should prove that trust controls are designed and operating.

Typical Records

  • System description
  • Trust criteria mapping
  • Information security policy
  • Access review records
  • Change approval tickets
  • Incident response records
  • Vendor risk reviews
  • Backup test evidence
  • Monitoring logs
  • Management assertion draft
Records should be current, controlled and easy for the responsible team to maintain.

Common Mistakes to Avoid

These weaknesses often delay certification, customer review or audit readiness when they are left unresolved.

  • Selecting too many criteria without matching commitments or evidence.
  • Confusing policy existence with control operation.
  • Not retaining evidence during the reporting period.
  • Leaving vendor risk reviews informal.
  • Starting SOC 2 readiness after customers have already requested a report.
Correcting these issues early can reduce repeated document rework and audit findings.
Related Services

For related requirements, review ISO 27001 certification consulting services in Turkey where shared teams, records or audit evidence can support the same Turkey operation.

For related requirements, review VAPT certification consulting company in Turkey where shared teams, records or audit evidence can support the same Turkey operation.

For related requirements, review SOC 1 certification consulting services in Turkey where shared teams, records or audit evidence can support the same Turkey operation.

FAQs

SOC 2 Questions from Turkey Service Providers

These answers focus on Trust Services Criteria, control evidence and reporting readiness.

What is SOC 2 used for?

SOC 2 reports provide assurance over service organisation controls related to Trust Services Criteria such as security, availability, confidentiality, processing integrity and privacy.

Which SOC 2 criteria should we choose?

Security is commonly included, while other criteria should match customer commitments, contractual obligations and service risks.

What is the difference between SOC 2 Type 1 and Type 2?

Type 1 evaluates control design at a point in time. Type 2 evaluates design and operating effectiveness over a defined period.

Is SOC 2 a certification?

SOC 2 is an attestation report issued by an independent auditor, not an ISO-style certification, but many customers treat it as assurance evidence.

What controls are commonly reviewed?

Common controls include access management, change management, incident response, monitoring, backup, vendor risk, risk assessment and security awareness.

Can ISO 27001 help SOC 2 readiness?

Yes. ISO 27001 controls can provide useful evidence, but SOC 2 still requires mapping to Trust Services Criteria and report scope.

Does SOC 2 require penetration testing?

Penetration testing is often used as evidence for security monitoring and vulnerability management, depending on scope and risk.

What is a system description?

It describes the services, infrastructure, people, processes, data and controls included in the SOC 2 report scope.

How long does evidence need to be collected?

For Type 2 reports, evidence is collected across the chosen reporting period, often several months.

How does Qualitcert support SOC 2 in Turkey?

Qualitcert supports scope definition, criteria mapping, policy development, evidence planning, readiness testing and audit preparation.

Speak with Qualitcert

Prepare SOC 2 Trust Services Readiness in Turkey

Share your service scope, customer commitments and current security evidence. Qualitcert can help map SOC 2 controls and prepare your team for audit readiness.

Request a Consultation →
Scroll to Top