Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

turkey

Consulting &

ISO Certifications

-ISO Certification-

SOC I Certification Consulting Services in Turkey

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

To help companies show their dedication to operational efficiency and strong internal controls, Qualitcert provides full SOC I certification consulting services in Turkey. This certification, which is targeted primarily at service firms, gives clients peace of mind about the dependability and security of their financial reporting procedures and controls. In close collaboration with clients, Qualitcert’s team of seasoned consultants evaluates current systems and procedures to pinpoint areas for enhancement and guarantee adherence to the exacting standards established by the American Institute of Certified Public Accountants (AICPA). Qualitcert enables enterprises to effectively acquire SOC I certification through a structured methodology that includes risk assessment, gap analysis, and customized recommendations. Businesses can acquire a competitive advantage in the market and boost their credibility by obtaining this accreditation, which promotes

Get In Touch

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

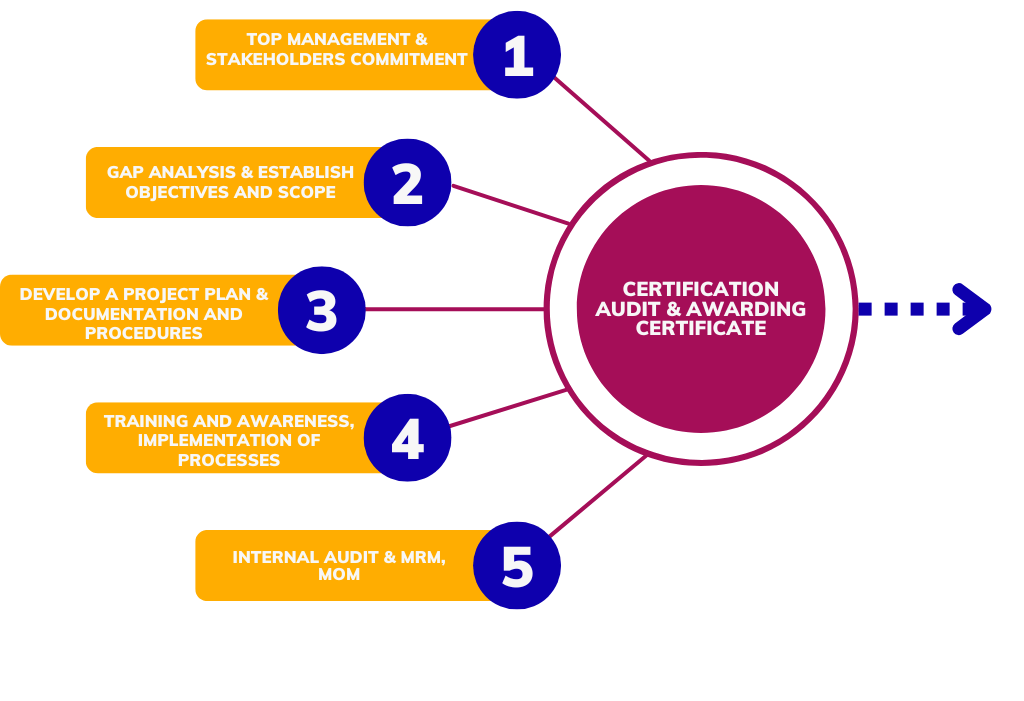
Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
Financial Reporting Control Assurance

SOC 1 Certification Consulting Services in Turkey for Internal Controls over Financial Reporting

SOC 1 readiness helps service organisations in Turkey document, test and improve controls that can affect clients’ financial reporting processes.

Control assurance for financial reporting reliance

SOC 1 consulting services in Turkey focus on internal controls over financial reporting, especially where a service organisation processes transactions, payroll, billing, claims, accounting data or fund administration on behalf of clients.

The report is not a general cybersecurity certificate. It is designed for user entities and their auditors who need assurance about controls relevant to financial statements.

Qualitcert helps teams define system boundaries, control objectives, process flows, control descriptions, evidence requirements and readiness testing before a formal SOC 1 examination.

The work should produce a clear control narrative, consistent evidence and management accountability for control operation over the reporting period.

Turkey Context

SOC 1 Needs for Turkey Service Organisations

Turkey service providers supporting finance, payroll, outsourcing, technology-enabled accounting and transaction processing may be asked for SOC 1 assurance by enterprise clients.

Clients need to know whether outsourced activities could affect the completeness, accuracy, authorisation or reporting of financial information.

SOC 1 readiness helps service organisations turn informal reviews, reconciliations and approvals into described controls with owners, frequency and evidence.

For businesses serving multinational or regulated customers, a well-prepared SOC 1 control environment can reduce repeated audit requests and improve client confidence.

Operational Value

SOC 1 Benefits for Turkey Service Providers

SOC 1 supports client assurance where financial reporting controls are outsourced.

Clear control accountability

Owners, frequencies and evidence expectations are defined for each control.

Reduced client audit pressure

A SOC 1 report can support multiple client assurance requests.

Improved process discipline

Reconciliations, approvals and exception handling become more consistent.

Stronger financial control confidence

Clients gain assurance over financially relevant service processes.

Industry Applications

SOC 1 Applications in Turkey

SOC 1 is most relevant when services influence clients’ financial records or reporting.

01

Payroll processors

Salary calculations, approvals, bank files and statutory deduction controls.

02

Accounting outsourcing

Journal processing, reconciliations, review controls and reporting support.

03

Payment service providers

Transaction completeness, settlement, exception handling and reconciliation.

04

Claims administrators

Claim authorisation, calculation, payment and reporting controls.

05

Fund administration

NAV support, investor records, reconciliations and reporting controls.

06

ERP service providers

Change control, access, job processing and financial data interfaces.

Certification Journey

SOC 1 Readiness Journey

The route focuses on system description, controls and evidence over time.

01

Define report scope

Identify services, systems, locations, users and financially relevant processes.

02

Map control objectives

Link process risks with financial reporting control objectives.

03

Document controls

Prepare control descriptions, owners, frequency and evidence expectations.

04

Test readiness

Review sample evidence and identify control design or operating gaps.

05

Remediate issues

Improve approvals, reconciliations, access controls and exception handling.

06

Support examination

Organise evidence for the independent SOC 1 auditor.

Documentation and Evidence

SOC 1 Control Documentation and Evidence

Evidence should show that controls are suitably designed and consistently operated.

Typical Records

  • System description
  • Control matrix
  • Process flow diagrams
  • User access reviews
  • Transaction reconciliation records
  • Approval evidence
  • Exception logs
  • Change management tickets
  • Incident records
  • Management assertion draft
Records should be current, controlled and easy for the responsible team to maintain.

Common Mistakes to Avoid

These weaknesses often delay certification, customer review or audit readiness when they are left unresolved.

  • Confusing SOC 1 with SOC 2 or ISO 27001.
  • Defining controls without evidence that can be tested.
  • Leaving outsourced subservice activities unclear.
  • Relying on verbal approvals instead of retained evidence.
  • Starting readiness too close to the reporting period end.
Correcting these issues early can reduce repeated document rework and audit findings.
Related Services

For related requirements, review SOC 2 certification consulting services in Turkey where shared teams, records or audit evidence can support the same Turkey operation.

For related requirements, review ISO 27001 certification consulting services in Turkey where shared teams, records or audit evidence can support the same Turkey operation.

For related requirements, review VAPT certification consulting company in Turkey where shared teams, records or audit evidence can support the same Turkey operation.

FAQs

SOC 1 Questions from Turkey Service Organisations

These answers focus on financial reporting controls and readiness preparation.

What is SOC 1 used for?

SOC 1 reports provide assurance over controls at a service organisation that may affect user entities’ internal control over financial reporting.

Is SOC 1 the same as SOC 2?

No. SOC 1 focuses on financial reporting controls, while SOC 2 focuses on Trust Services Criteria such as security, availability and confidentiality.

Who needs SOC 1 readiness?

Payroll processors, accounting outsourcers, claims administrators, payment processors, fund administrators and financial system providers may need SOC 1 readiness.

What is a control objective?

A control objective describes what a set of controls is intended to achieve, such as complete and accurate transaction processing.

What evidence is needed for SOC 1?

Evidence may include approvals, reconciliations, access reviews, exception logs, change records, incident records and management review evidence.

What is a Type 1 SOC 1 report?

A Type 1 report evaluates control design at a specific point in time.

What is a Type 2 SOC 1 report?

A Type 2 report evaluates both design and operating effectiveness over a defined period.

Can ISO 27001 evidence support SOC 1?

Some IT general controls may overlap, but SOC 1 must still focus on financial reporting risks and control objectives.

How early should readiness begin?

Readiness should begin before the reporting period so controls can operate consistently and evidence can be collected.

How does Qualitcert support SOC 1 in Turkey?

Qualitcert supports scope definition, control mapping, documentation, evidence readiness, gap remediation and audit preparation.

Speak with Qualitcert

Prepare SOC 1 Readiness for Turkey Service Operations

Share your client services, transaction flows and existing control evidence. Qualitcert can help organise SOC 1 readiness around financial reporting control objectives.

Request a Consultation →
Scroll to Top