
An ISMS built on risk, assets and accountability
ISO 27001 certification services in Turkey begin by defining what information needs protection: customer data, contracts, source code, financial records, production data, cloud services, devices, networks and supplier-accessed systems.
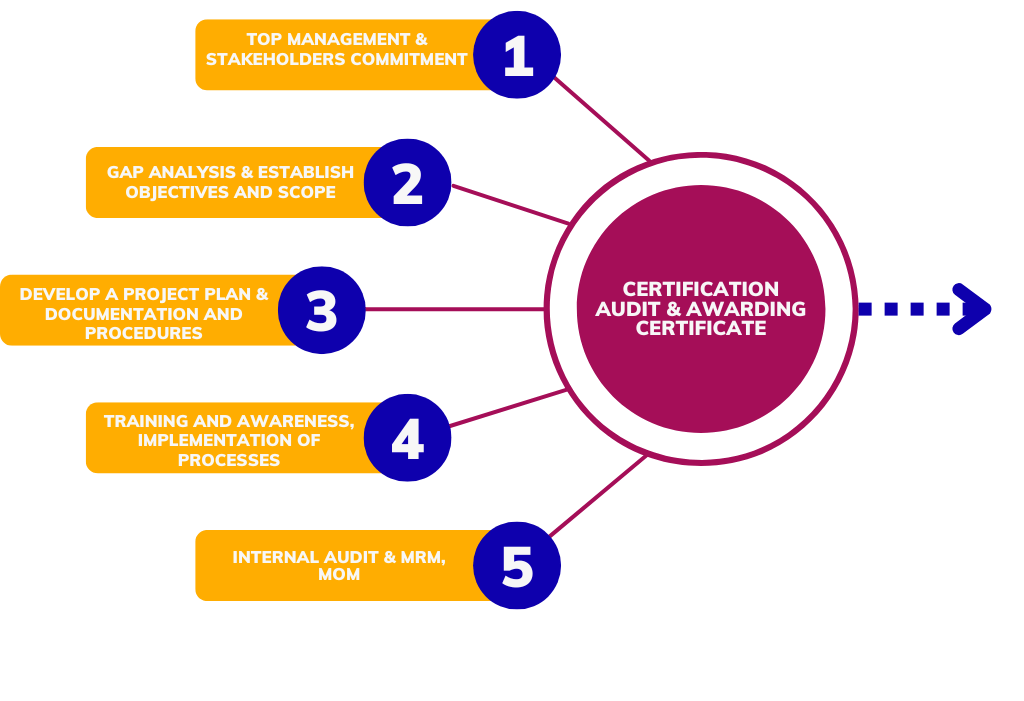
The standard is not limited to IT. It requires leadership commitment, risk treatment, access control, supplier security, awareness, incident response and documented evidence that controls are selected and monitored.
Qualitcert supports ISMS scoping, asset identification, risk assessment methodology, statement of applicability preparation, Annex A control mapping, internal audit and certification readiness.
The outcome is a security management system that helps organisations make defensible decisions about confidentiality, integrity and availability.