
ISO Certifications
Nigeria
Consulting &
ISO Certifications
-ISO Certification-
QUALIT
CERT
CONSULTING AND ISO CERTIFICATIONS
Qualitcert provides specialized SOC I certification services in Nigeria, designed to help organizations enhance their internal controls over financial reporting. Their expert consultants conduct a thorough gap analysis to assess existing systems and identify areas for improvement. Following this, they assist in developing and implementing effective controls and processes that comply with SOC I requirements. Qualitcert ensures that organizations are well-prepared for the SOC I audit by helping to create comprehensive documentation and evidence of compliance. They offer staff training to ensure understanding and proper execution of the controls. Throughout the certification process, Qualitcert’s consultants provide ongoing support, guiding organizations through each step to achieve SOC I certification successfully. This certification helps organizations demonstrate their commitment to maintaining robust internal controls, thereby increasing trust and confidence among clients and stakeholders.
Please Reach Us Today
Approach and Methodology used to implement Management System Standard
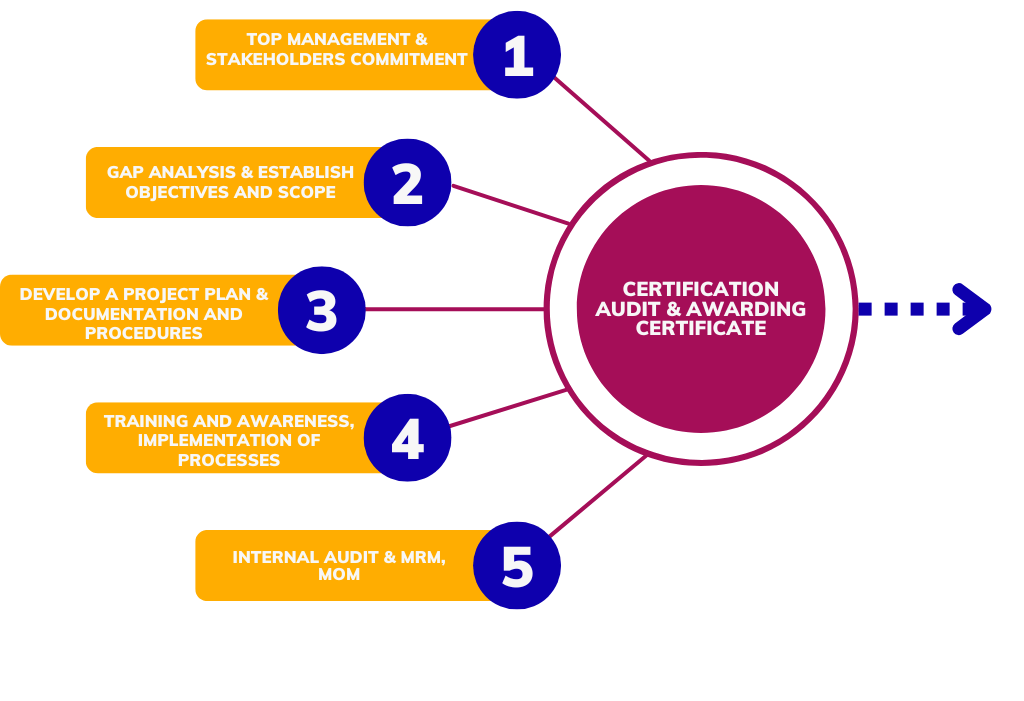
Implementing an SOC I standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the SOC I standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
SOC 1 Readiness Services in Nigeria for Controls Affecting Financial Reporting
SOC 1 helps Nigerian service organisations demonstrate that controls relevant to customers' financial reporting are suitably designed and, for Type II, operating effectively.
Define the controls that matter to user organisations and their auditors
A SOC 1 examination addresses controls at a service organisation that are relevant to user entities' internal control over financial reporting. The report is intended for customers, their auditors and specified users rather than general marketing distribution.
Nigerian payroll processors, transaction platforms, fund administrators, claims processors, data centres and outsourced finance providers may perform activities that feed directly into customer ledgers, balances or financial disclosures. Control failures can therefore affect more than service availability.
Readiness begins by defining the service, system boundaries, control objectives, subservice organisations and complementary user-entity controls. Management then prepares a system description and maps controls to the risks that could cause inaccurate, incomplete, unauthorised or untimely processing.
Qualitcert supports scope workshops, control mapping, evidence design, walkthroughs, remediation and readiness assessment before an independent attestation engagement.
Assurance for outsourced processes that enter the financial close
Customers increasingly expect service providers to explain how transaction integrity, authorisation, reconciliation and change controls are maintained.
Controls may cover input validation, approval, processing completeness, exception handling, reconciliations, interface monitoring, report generation and access to financially relevant systems.
Technology general controls often support these objectives. User provisioning, privileged access, program changes, batch monitoring, backup and incident handling may be included when they affect financial processing.
A Type I report evaluates design at a point in time. A Type II report also tests operating effectiveness over a period, so evidence must be generated consistently rather than assembled at the end.
Why service organisations pursue SOC 1 readiness
The report can reduce repeated customer audit effort when the service genuinely affects financial-reporting controls.
Clearer customer assurance
A structured report explains relevant controls and testing to user entities and their auditors.
Better control accountability
Owners, frequencies, evidence and exception criteria are defined for financially relevant activities.
Reduced audit disruption
Reusable assurance evidence can replace multiple overlapping customer control reviews.
Stronger process discipline
Reconciliations, approvals, access and change controls become more consistent and reviewable.
Nigerian service scenarios where SOC 1 may be relevant
SOC 1 applies when the outsourced service can materially influence a customer's financial statements or ICFR.
Payroll service providers
Control authorised inputs, payroll calculations, changes, exception review, payment files and reconciliation.
Payment and transaction processors
Demonstrate transaction completeness, settlement controls, interface monitoring and restricted access.
Fund and pension administrators
Manage valuations, contributions, benefit processing, reconciliations and financial report outputs.
Claims processing services
Control claim data, authorisation, calculation, payment interfaces and exception resolution.
Finance and accounting outsourcing
Standardise journal support, approval, close activities, reconciliations and customer reporting.
Data hosting for financial systems
Evidence logical access, change control, job processing, backup and incident controls relevant to customers.
From ICFR impact analysis to examination-ready evidence
The preparation route begins with the service's financial-reporting effect and ends with sustainable control operation.
Confirm report users and scope
Define services, systems, locations, subservice organisations and intended user entities.
Map ICFR-related risks
Identify how errors or unauthorised activity could affect transaction and reporting assertions.
Define objectives and controls
Document control purpose, owner, frequency, evidence, population and exception handling.
Prepare the system description
Describe services, infrastructure, people, procedures, data and control boundaries accurately.
Operate and test readiness
Collect evidence, sample controls, resolve gaps and confirm complementary user entity controls.
Support the examination
Coordinate management assertion, requests, exceptions and remediation with the assurance practitioner.
Records needed for financial-control assurance readiness
Evidence should be complete enough for an examiner to identify the control population, select samples and verify operation.
Typical SOC 1 readiness evidence
- Service and system scope
- ICFR risk and control matrix
- System description
- Control owner register
- Transaction processing logs
- Approval and reconciliation records
- Access review evidence
- Change management records
- Exception and incident records
- Management assertion support
SOC 1 readiness errors
Organisations lose time when the control description is broader than the available evidence or the report is used for the wrong assurance purpose.
- Treating SOC 1 as a general cybersecurity report.
- Including controls that do not affect user-entity financial reporting.
- Describing reviews without documenting criteria and follow-up.
- Ignoring complementary user entity and subservice-organisation controls.
- Starting a Type II period before controls operate consistently.
Related SOC 1 Services for Nigerian Organisations
For a connected requirement, review SOC 2 consulting services in Nigeria to coordinate shared governance, records and management responsibilities.
For a connected requirement, review ISO/IEC 27001 consulting services in Nigeria where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review ISO 9001 consulting services in Nigeria to reduce duplicated work and build a more coherent assurance programme.
SOC 1 questions from service organisations in Nigeria
These answers cover ICFR relevance, Type I and Type II reports, controls and user responsibilities.
What is a SOC 1 report used for?
It provides assurance over controls at a service organisation that are relevant to user entities' internal control over financial reporting.
Who typically requests SOC 1 assurance?
Customers whose financial reporting depends on the outsourced service, as well as their finance teams and external auditors, commonly request it.
What is the difference between SOC 1 Type I and Type II?
Type I addresses control design at a specified date, while Type II also tests operating effectiveness over a defined review period.
Is SOC 1 a certification?
SOC 1 is an independent assurance report rather than an ISO-style management-system certificate.
What are complementary user entity controls?
They are controls that customers must operate for the service organisation's controls and objectives to work as intended.
Can cybersecurity controls appear in SOC 1?
Yes, but only where they are relevant to financial-reporting risk, such as access or change controls over financially significant systems.
What should a system description include?
It should describe the service, infrastructure, software, people, procedures, data, boundaries, control objectives and relevant subservice organisations.
How long is a SOC 1 Type II review period?
The period is agreed for the engagement and should be long enough to provide meaningful operating-effectiveness evidence.
What happens when a control exception is found?
The examiner evaluates the nature and impact. Management should understand the cause, affected population, compensating controls and corrective action.
How can Qualitcert support SOC 1 readiness in Nigeria?
Qualitcert can help with scope, risk-control mapping, system descriptions, evidence preparation, readiness testing and remediation planning.
Define a SOC 1 Readiness Programme for Your Nigerian Service
Share your service description, customer commitments, process flows and existing controls. Qualitcert can help establish a defensible SOC 1 scope and remediation plan.