Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

Ang

ola

Consulting &

ISO Certifications

-ISO Certification-

VAPT Certification Consulting Company in Angola

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

Qualitcert offers specialized VAPT (Vulnerability Assessment and Penetration Testing) certification services in Angola, focusing on helping organizations enhance their cybersecurity posture and resilience against potential threats. As a leading consultancy, Qualitcert provides comprehensive VAPT services including vulnerability assessments, penetration testing, security audits, remediation guidance, and training for IT teams and management. Their tailored approach ensures that businesses in Angola can identify and mitigate security vulnerabilities, protect sensitive data, and comply with industry standards and regulatory requirements. With a team of experienced cybersecurity experts, Qualitcert guides clients through every step of the VAPT certification process, from initial assessment to successful implementation of robust security measures. By partnering with Qualitcert for VAPT certification consulting, organizations in Angola can strengthen their defenses, safeguard their IT infrastructure, and maintain trust and confidence among their stakeholders.

Please Reach Us Today

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

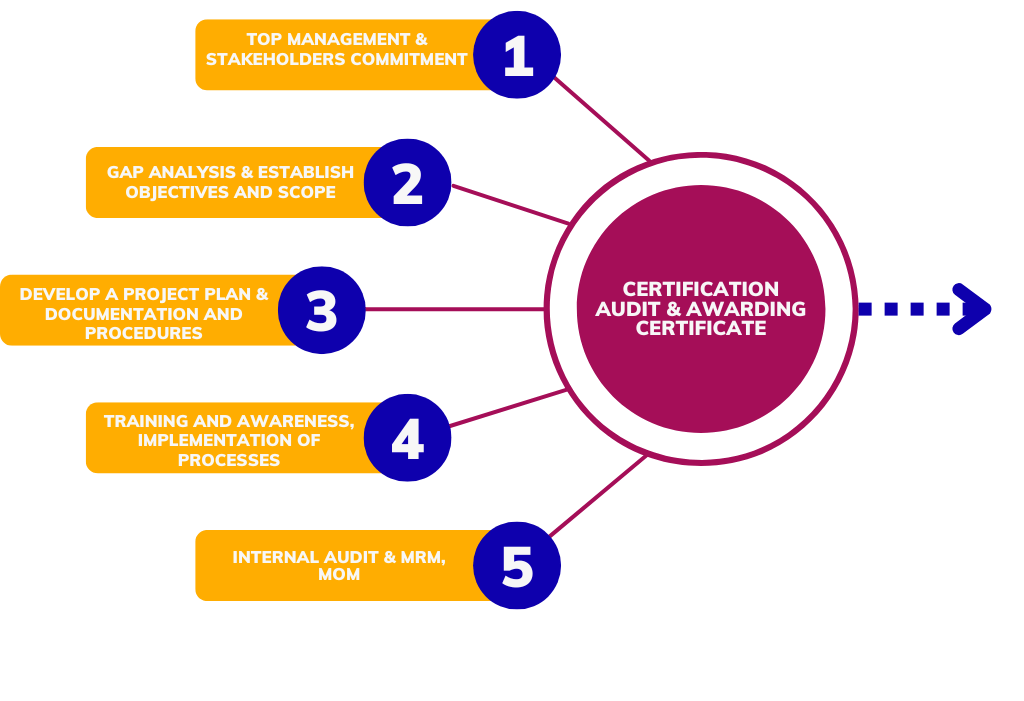
Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an VAPT  standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the VAPT standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
Technical Security Testing in Angola

VAPT Consulting Services in Angola for Verified Vulnerabilities and Attack Paths

VAPT combines systematic vulnerability assessment with controlled penetration testing to reveal exploitable weaknesses and prioritise remediation.

Move from automated findings to validated attack paths

Vulnerability assessment identifies weaknesses across defined assets, while penetration testing safely attempts exploitation to confirm attack paths and business impact.

Organisations in Angola expose websites, APIs, mobile applications, remote-access gateways, cloud services and internal systems to different threat scenarios.

A controlled engagement defines scope, test windows, permitted techniques, excluded systems, data-handling rules, contacts and stopping conditions.

Qualitcert supports external, internal, web, API, mobile and cloud testing followed by risk-ranked reporting, remediation guidance and retesting.

Angolana Digital Exposure

Testing attack paths across Angola's connected services

Digital banking, public portals, industrial remote access and third-party integrations can create exposures that configuration reviews do not reveal.

Authentication and authorisation require attention because weak sessions, password recovery and excessive privileges can expose sensitive information.

APIs and mobile back ends should be assessed for token handling, rate limits, input validation, data exposure and transaction logic.

Findings should identify affected assets, reproduction steps, likely impact, root conditions and recommended fixes, followed by retesting.

Security Testing Outcomes

What disciplined VAPT provides

The value comes from validated findings and clear remediation priorities rather than raw vulnerability counts.

Verified technical risk

Manual testing separates exploitable issues from false positives and low-value scanner noise.

Prioritised remediation

Severity, exposure, exploitability and business impact guide practical action sequencing.

Stronger customer assurance

Reports and retest evidence support due diligence, compliance and contractual security expectations.

Improved engineering feedback

Root causes and attack paths help development and infrastructure teams prevent recurrence.

Testing Scenarios

VAPT applications for organisations in Angolana

The testing method should match the asset type, threat model, authentication level and operational sensitivity.

01

Banks and payment services

Test customer applications, transaction APIs, portals and internal attack paths.

02

Telecommunications

Assess subscriber platforms, exposed services, remote access and infrastructure.

03

Oil and gas companies

Evaluate internet exposure, remote administration, suppliers and critical systems.

04

Government services

Test citizen portals, public applications and high-value systems.

05

Healthcare organisations

Assess patient systems, remote access and sensitive applications.

06

Cloud and software providers

Test applications, infrastructure, identity, APIs and deployment controls.

Testing Methodology

A controlled route from scope to retest

The engagement protects operational stability while producing reproducible and decision-ready evidence.

01

Authorise and scope

Define assets, dates, methods, credentials, exclusions, contacts, data handling and stop conditions.

02

Discover the attack surface

Identify reachable hosts, services, applications, APIs, versions and exposed functionality.

03

Assess vulnerabilities

Use appropriate tools and manual analysis to identify configuration, code and control weaknesses.

04

Validate exploitation safely

Confirm material findings and attack paths without exceeding agreed operational limits.

05

Report and remediate

Document evidence, impact, severity, root cause and prioritised corrective recommendations.

06

Retest closed findings

Verify remediation, identify residual exposure and issue updated status evidence.

VAPT Deliverables

Technical records expected from a professional engagement

Deliverables should be suitable for executives, risk owners and technical teams without exposing unnecessary sensitive detail.

Typical VAPT documentation

  • Signed rules of engagement
  • Authorised asset list
  • Testing methodology
  • Credential and access plan
  • Finding evidence
  • Risk and severity rationale
  • Executive summary
  • Technical remediation guidance
  • Finding owner tracker
  • Retest confirmation report
Sensitive exploit details, credentials and screenshots should be handled through controlled channels and retained only as agreed.

Security testing mistakes

Poorly planned testing can produce misleading results or unnecessary operational risk.

  • Running scans without written authorisation and scope boundaries.
  • Calling automated scanning a full penetration test.
  • Testing only IP addresses while ignoring applications and APIs.
  • Ranking findings by scanner score without business context.
  • Closing findings from screenshots without a controlled retest.
Best practice includes safe coordination, validated evidence, clear ownership and retesting of material corrections.
Security Management Links

For a connected requirement, review ISO/IEC 27001 certification consulting services in Angola to coordinate shared governance, documentation and management responsibilities.

For a connected requirement, review SOC 2 certification consulting services in Angola where common risks, suppliers or operational controls should be aligned.

For a connected requirement, review ISO 9001 certification consulting services in Angola to reduce duplicated work and build a coherent assurance programme.

VAPT FAQs

VAPT questions from organisations in Angolana

These answers explain scope, scanning, penetration testing, reporting and remediation.

What is the difference between vulnerability assessment and penetration testing?

Vulnerability assessment identifies potential weaknesses, while penetration testing manually validates exploitability and attack impact within authorised limits.

Is an automated scan enough for VAPT?

No. Automated tools are useful, but professional testing includes manual verification, logic testing, attack-path analysis and false-positive review.

What systems can be included in VAPT?

Scope may include external or internal networks, web applications, APIs, mobile apps, cloud environments and wireless systems.

Is VAPT safe for production systems?

It can be performed safely with agreed methods, timing, stop conditions and exclusions, but residual operational risk must be assessed before testing.

What is authenticated vulnerability testing?

It uses approved credentials to inspect patching, configurations and privileges that cannot be assessed accurately from an unauthenticated position.

How are vulnerabilities prioritised?

Priority should consider technical severity, exposure, exploitability, affected data or service, compensating controls and business impact.

What should a penetration-test report contain?

It should include scope, methodology, executive findings, technical evidence, risk rationale, remediation guidance and limitations.

Why is retesting important?

Retesting confirms that the specific weakness and related attack path were removed rather than relying only on implementation statements.

How often should VAPT be performed?

Frequency should reflect risk, system change, contractual obligations and threat exposure. Major changes can trigger testing outside the routine cycle.

How does Qualitcert support VAPT in Angolana?

Qualitcert can help define scope, coordinate testing, present prioritised findings, support remediation tracking and verify closure through retesting.

Test What Attackers Can Reach

Define a Controlled VAPT Scope for Your Angola Systems

Share your asset list, architecture and testing constraints. Qualitcert can help plan testing, prioritise findings and verify remediation.

Request a VAPT Scoping Call →
Scroll to Top