
ISO Certifications
jordan
Consulting &
ISO Certifications

-ISO Certification-
ISO 27001 Certification Consulting Services in Jordan
QUALIT
CERT
CONSULTING AND ISO CERTIFICATIONS
Qualitcert’s ISO 27001 Certification Services in Jordan provide businesses looking to implement and certify their information security management systems (ISMS) with all-encompassing help. Qualitcert offers services that assist businesses with every step of the certification process and guarantee adherence to the global standard for handling confidential company data. These services, which are all customized to match the unique needs of the customer, include gap analysis, risk assessment, documentation preparation, training, and internal audits. Qualitcert assists companies in Jordan in obtaining ISO 27001 certification in an efficient and effective manner while enhancing their reputation, client trust, and overall security posture. The company focuses on reducing security risks and enhancing data protection policies.
ISO Certification Process – Step by Step Guide
The ISO certification process helps organizations implement international standards to improve quality, safety, efficiency, and compliance. Below is a structured step-by-step ISO certification process followed by professional ISO consultants and certification bodies.
ISO Application
The organization submits an application for ISO certification and defines the scope of certification including departments, processes, and operations.
Gap Analysis
ISO consultants analyze the current management system and identify gaps between existing processes and ISO standard requirements.
ISO Documentation
Preparation of ISO manuals, procedures, policies, risk assessments, and records required to comply with ISO standards.
System Implementation
ISO processes are implemented across departments with employee training, process control, and compliance monitoring.
Internal Audit
Internal auditors review the management system to verify compliance and identify corrective actions before the certification audit.
Management Review
Top management evaluates the effectiveness of the ISO management system and ensures readiness for certification.
Certification Audit
An accredited certification body conducts an external audit to verify compliance with ISO standards.
ISO Certification
After successful audit completion, the organization receives the official ISO certificate demonstrating compliance with international standards.
Surveillance Audits
Annual surveillance audits ensure continuous compliance and improvement of the ISO management system.
Get In Touch
Approach and Methodology used to implement Management System Standard
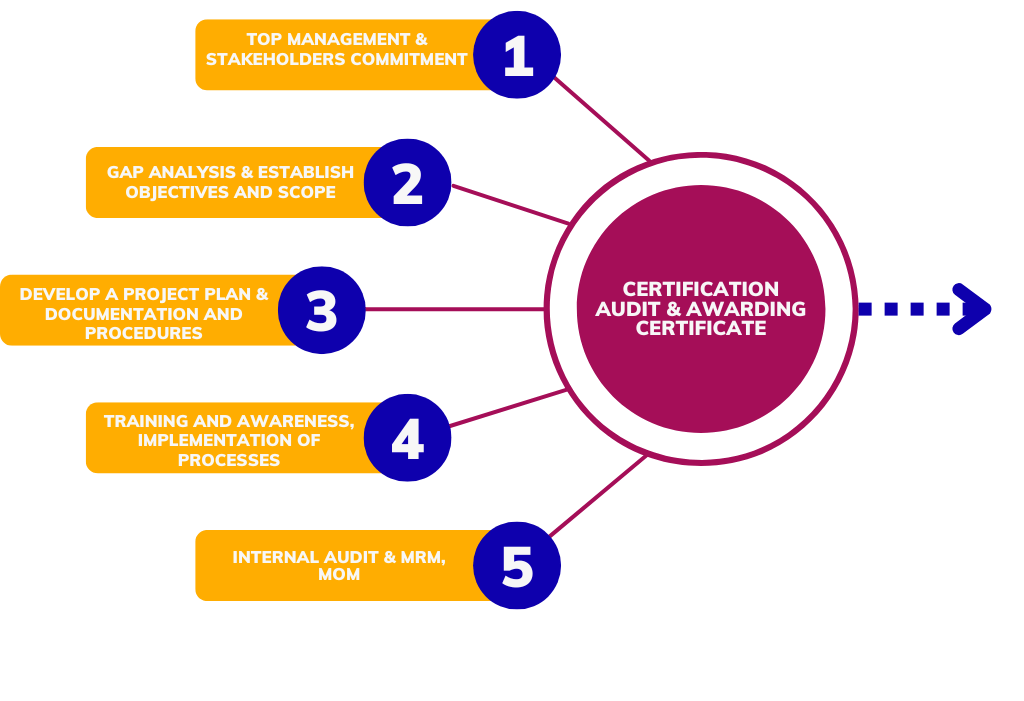
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
ISO/IEC 27001: Build a Practical Information Security Management System for Jordan
For organisations across Jordan, ISO/IEC 27001 provides a structured way to govern information-security risks, assets, access, suppliers, incidents and continuity, with controls adapted to professional offices, pharmaceutical and food facilities, logistics operations, hospitals, technology teams and regional branches.
ISO/IEC 27001 Implementation Aligned with the Operating Environment in Jordan
The operating environment in Jordan combines pharmaceuticals and healthcare, information technology and services, food and consumer manufacturing, logistics and trade. This creates different priorities for each organisation, but ISO/IEC 27001 provides a common structure for teams that need to govern information-security risks, assets, access, suppliers, incidents and continuity.
Businesses may connect Amman-based management with industrial estates, regional facilities, export activities and cross-border logistics. The system should define who performs each control, what evidence is retained and how performance is evaluated when conditions or business requirements change.
Qualitcert supports organisations in Jordan by adapting the implementation work to digital services, customer information, cloud platforms, operational systems and third-party access. The service focuses on practical preparation, documented controls, internal review and readiness for the relevant independent assessment.
Implementation Priorities for ISO/IEC 27001 in Jordan
The system should reflect export-oriented manufacturing, regional logistics, healthcare and pharmaceutical operations and professional and technology services.
Risk-Based Control Selection
Link security controls to documented risks rather than applying a generic checklist without business context. In Jordan, this is especially relevant where organisations manage export-oriented manufacturing.
Access and Identity Governance
Control joiners, movers, leavers, privileged accounts, remote access and periodic access reviews. In Jordan, this is especially relevant where organisations manage regional logistics.
Supplier and Cloud Assurance
Evaluate technology providers, hosting partners and processors whose services affect protected information. In Jordan, this is especially relevant where organisations manage healthcare and pharmaceutical operations.
Incident and Continuity Readiness
Define escalation, investigation, communication, recovery and lessons-learned activities before an incident occurs. In Jordan, this is especially relevant where organisations manage professional and technology services.
ISO/IEC 27001 Applications Across Key Sectors in Jordan
The exact controls should be adapted to the sector, operating model, customer commitments and risks present in Jordan.
Pharmaceuticals and Healthcare
Apply information assets, access rights, supplier connections, incident handling and continuity across sensitive records, specialist equipment, competence, suppliers and continuity-sensitive services, with evidence matched to the services and operating risks present in Jordan.
Information Technology and Services
Control information assets, access rights, supplier connections, incident handling and continuity across cloud platforms, software changes, digital services, data flows, vendors and remote access, with evidence matched to the services and operating risks present in Jordan.
Food and Consumer Manufacturing
Document information assets, access rights, supplier connections, incident handling and continuity across suppliers, processing, storage, handling, distribution and customer-facing food operations, with evidence matched to the services and operating risks present in Jordan.
Logistics and Trade
Verify information assets, access rights, supplier connections, incident handling and continuity across shipments, warehouses, fleets, partner interfaces and time-sensitive service handovers, with evidence matched to the services and operating risks present in Jordan.
Construction and Engineering
Strengthen information assets, access rights, supplier connections, incident handling and continuity across project planning, contractors, materials, inspections, changing site conditions and handover, with evidence matched to the services and operating risks present in Jordan.
Tourism and Hospitality
Coordinate information assets, access rights, supplier connections, incident handling and continuity across guest or customer services, facilities, suppliers, payments, seasonal demand and multi-shift operations, with evidence matched to the services and operating risks present in Jordan.
A Structured Route to ISO/IEC 27001 Certification Readiness
The roadmap should be scaled to the certification scope, complexity and maturity of existing security practices.
Define Scope and Context
Identify locations, services, systems, interested parties and boundaries included in the ISMS.
Inventory Information Assets
Record important information, systems, owners, locations, dependencies and classification needs.
Assess Information Risks
Evaluate threats, vulnerabilities, likelihood and business impact using an agreed method.
Create the Risk Treatment Plan
Select treatments, assign owners, set deadlines and justify applicable controls.
Prepare the Statement of Applicability
Document control applicability, implementation status and reasons for inclusion or exclusion.
Implement Policies and Controls
Put approved technical, physical, organisational and people controls into routine operation.
Audit and Review the ISMS
Complete internal audit, management review, corrective action and evidence checks.
Prepare for Certification Audit
Organise records, brief process owners and address readiness gaps before the external audit.
Core ISO 27001 Documents and Readiness Considerations
The final document set depends on the scope and risk profile, but it must demonstrate that security decisions are controlled and traceable.
Typical ISMS Documents and Records
- ISMS scope and context analysis
- Information security policy
- Information asset inventory
- Risk assessment methodology
- Risk assessment results
- Risk treatment plan
- Statement of Applicability
- Access-control and user lifecycle records
- Supplier-security evaluation records
- Incident-management records
- Internal-audit and management-review records
- Corrective-action and improvement records
Scope, Effort and Timeline Factors
The required effort should be estimated from the actual scope and current level of readiness rather than from a single package applied to every organisation.
- Number of locations, systems and business services in scope
- Volume and sensitivity of information handled
- Cloud, outsourced and supplier dependencies
- Existing cybersecurity policies and technical controls
- Need for asset discovery and risk workshops
- Complexity of access, network and software environments
- Availability of operational evidence and monitoring records
- Internal-audit and certification-body audit requirements
Why Choose Qualitcert for ISO 27001 Implementation Support in Jordan?
Qualitcert helps convert information-security requirements into responsibilities and controls that can be used by management, IT teams, process owners and employees.
The support remains separate from the independent certification decision and focuses on implementation, documentation, internal review and audit readiness.
Scope Definition
Clarify the services, systems, locations and organisational boundaries included in the ISMS.
Risk Workshop Support
Develop a practical risk method and facilitate structured evaluation of information-security risks.
Control Mapping
Connect treatment decisions to policies, procedures, technical measures and accountable owners.
Evidence Readiness
Identify records needed to demonstrate that controls operate consistently over time.
Internal Audit Support
Evaluate conformity, implementation and unresolved gaps before certification assessment.
Continual Improvement
Build review, corrective-action and monitoring routines that continue after certification.
ISO/IEC 27001 Support Across Jordan
Support can be adapted for organisations operating from Amman, industrial estates, Aqaba-linked logistics operations, healthcare facilities and regional service locations.
Multi-site organisations should define how central policies, shared services and local operational controls are applied and evidenced.
ISO/IEC 27001 Questions from Organisations in Jordan
These answers provide general guidance for Jordan; the final scope depends on the organisation's activities, locations, risks and current evidence.
What is ISO/IEC 27001 used for?
ISO/IEC 27001 specifies requirements for an information security management system that helps an organisation manage risks to the confidentiality, integrity and availability of information.
How long does ISO 27001 implementation take in Jordan?
The period depends on scope, system complexity, number of locations, existing controls, risk-assessment maturity and the availability of evidence. A readiness assessment is needed before setting a reliable schedule. For Jordan, the estimate should also account for export-oriented manufacturing and regional logistics where relevant.
Is a vulnerability assessment enough for ISO 27001?
No. Technical testing may support risk evaluation, but ISO 27001 also requires governance, risk treatment, roles, competence, supplier controls, incident management, internal audit and management review.
What is the Statement of Applicability?
It is a controlled document that records which information-security controls are applicable, their implementation status and the justification for inclusion or exclusion.
Can ISO/IEC 27001 cover multiple operating locations in Jordan?
Yes. A multi-site ISMS can be considered when the central system, shared controls, site responsibilities and interfaces are clearly defined.
Does ISO 27001 require every system to be included?
Not necessarily. The organisation defines a justified ISMS scope, but exclusions and interfaces must be clear so that important risks are not omitted.
Can ISO 27001 be integrated with ISO 9001?
Yes. Common management-system elements such as document control, internal audit, management review, objectives and corrective action can be integrated.
What evidence is reviewed during an ISO 27001 audit?
Auditors may review risk records, the Statement of Applicability, access reviews, incident records, supplier evaluations, monitoring results, internal audits, management reviews and corrective actions.
Who issues the ISO 27001 certificate?
An independent certification body conducts the certification audit and makes the certification decision. Consultancy support should remain separate from that decision.
Are surveillance audits required after certification?
Yes. The organisation must maintain the ISMS and undergo periodic surveillance assessments during the certification cycle.
Plan Your ISO/IEC 27001 Readiness Review in Jordan
Share the activities, locations, systems, products or services you want included. Qualitcert can help define a practical scope for professional offices, pharmaceutical and food facilities, logistics operations, hospitals, technology teams and regional branches.