
ISO Certifications
jordan
Consulting &
ISO Certifications

-ISO Certification-
QUALIT
CERT
CONSULTING AND ISO CERTIFICATIONS
Qualitcert offers HITRUST Certification Consulting Services in Jordan to assist healthcare organizations in achieving HITRUST CSF (Common Security Framework) certification, a widely recognized standard for managing data protection and compliance in the healthcare sector. This certification integrates various regulatory requirements, including HIPAA, HITECH, and ISO standards, providing a comprehensive framework to ensure the security and privacy of sensitive health information. Qualitcert’s consulting services include assessing current security practices, developing tailored security policies, and implementing necessary controls to meet HITRUST requirements. By leveraging Qualitcert’s expertise, organizations can enhance their security posture, mitigate risks, and build trust with stakeholders while demonstrating their commitment to safeguarding patient data and complying with industry regulations. This support not only prepares businesses for the certification process but also fosters a culture of security and compliance within the organization.
ISO Certification Process – Step by Step Guide
The ISO certification process helps organizations implement international standards to improve quality, safety, efficiency, and compliance. Below is a structured step-by-step ISO certification process followed by professional ISO consultants and certification bodies.
ISO Application
The organization submits an application for ISO certification and defines the scope of certification including departments, processes, and operations.
Gap Analysis
ISO consultants analyze the current management system and identify gaps between existing processes and ISO standard requirements.
ISO Documentation
Preparation of ISO manuals, procedures, policies, risk assessments, and records required to comply with ISO standards.
System Implementation
ISO processes are implemented across departments with employee training, process control, and compliance monitoring.
Internal Audit
Internal auditors review the management system to verify compliance and identify corrective actions before the certification audit.
Management Review
Top management evaluates the effectiveness of the ISO management system and ensures readiness for certification.
Certification Audit
An accredited certification body conducts an external audit to verify compliance with ISO standards.
ISO Certification
After successful audit completion, the organization receives the official ISO certificate demonstrating compliance with international standards.
Surveillance Audits
Annual surveillance audits ensure continuous compliance and improvement of the ISO management system.
Get In Touch
Approach and Methodology used to implement Management System Standard
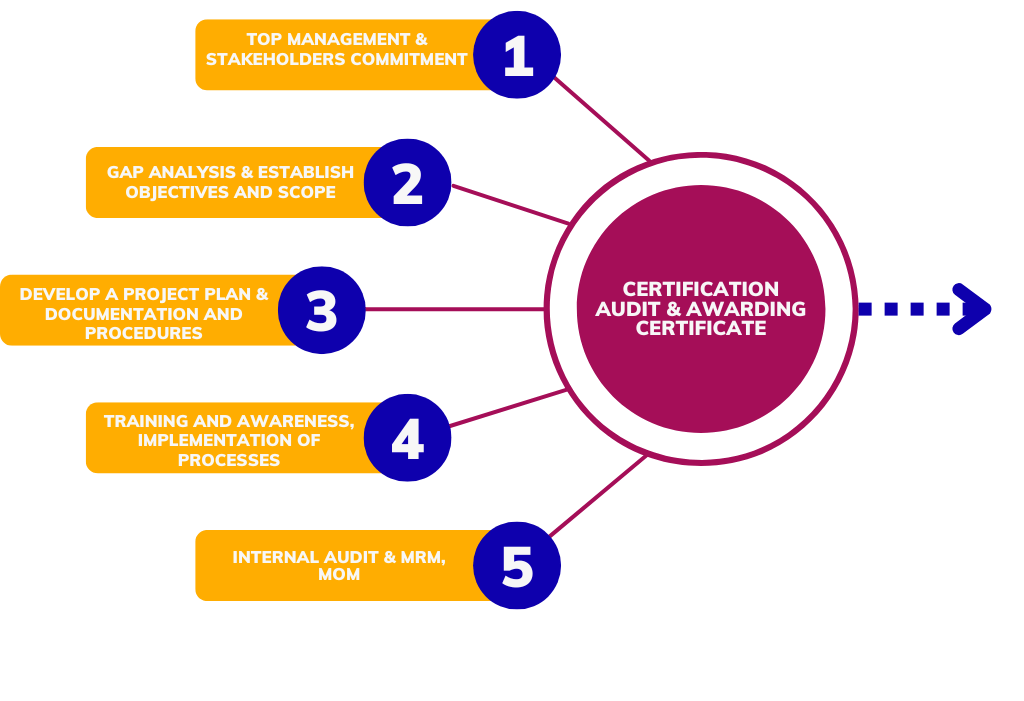
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
HITRUST Consulting and Readiness Services in Jordan
Build a practical HITRUST CSF assurance programme that helps Jordan organisations organise healthcare and security requirements into a scoped, evidence-based HITRUST assessment programme with clear ownership, current evidence and assessment readiness.
Build a Scaled HITRUST Evidence Programme for Health Data
Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Healthcare technology, analytics, cloud and outsourced-service providers in Jordan may use HITRUST to consolidate health-data assurance requirements. Successful HITRUST work begins with scope. The organisation must be clear about which activities, sites, products, systems and third parties belong within the HITRUST CSF assurance programme.
Once scope is established, Qualitcert evaluates the risks and obligations associated with assessment scope and factors, CSF requirement statements and policy and procedure maturity.
Procedures and evidence are then developed around implemented controls and measured and managed evidence, with practical checks to confirm that stated controls match actual behaviour.
The final stage reviews remediation and assessment support, open actions and management oversight so the organisation can approach the HITRUST assessment with a coherent evidence trail.
HITRUST Readiness for Jordan Healthcare Technology and Service Providers
Jordan organisations use HITRUST to improve assurance where assessment scope and factors, CSF requirement statements and policy and procedure maturity cross teams, suppliers or technical systems.
Healthcare assurance programmes need a scoped evidence model that brings policy, procedure, implementation, measurement and management together.
Common readiness problems arise when assessment scope and factors is treated separately from CSF requirement statements and policy and procedure maturity, creating duplicated controls or incomplete evidence.
Qualitcert structures the work so implemented controls, measured and managed evidence and remediation and assessment support can be reviewed together by operational leaders and specialist teams.
Operational Benefits of HITRUST in Jordan
The value comes from making assessment scope and factors, CSF requirement statements and policy and procedure maturity easier to manage, measure and explain.
Clearer Assessment Scope And Factors
Defines ownership, criteria and evidence for assessment scope and factors across the agreed scope.
Stronger Csf Requirement Statements
Connects CSF requirement statements to practical controls rather than isolated policy statements.
More Reliable Policy And Procedure Maturity
Makes policy and procedure maturity easier to monitor, test and improve with current records.
Better Implemented Controls
Supports consistent decisions about implemented controls during normal work and change.
Where HITRUST Applies in Jordan
The examples below show how the HITRUST CSF assurance programme changes with the operating model, risk profile and evidence needs of each sector.
Healthcare Technology and Cloud Services
Map health-data safeguards, maturity evidence, suppliers and assessment requirements.
Healthcare BPO
Protect health information across staff, facilities, endpoints and subcontractors.
Hospitals and Provider Networks
Coordinate clinical, administrative, infrastructure and third-party safeguards.
Health Analytics
Govern datasets, access, exports, de-identification and customer commitments.
Cloud Services for Healthcare
Address shared responsibility, infrastructure controls, logging and customer assurance.
Payer and Benefits Services
Manage member data, claims, interfaces, workforce access and service providers.
How HITRUST Readiness Is Built
The sequence moves from scope and current-state review to operating evidence and preparation for the HITRUST assessment.
Define Assessment Scope And Factors
Confirm boundaries, responsibilities and criteria for assessment scope and factors.
Assess Csf Requirement Statements
Review current practices, risks and evidence relating to CSF requirement statements.
Design Policy And Procedure Maturity
Create proportionate controls and records for policy and procedure maturity.
Implement Implemented Controls
Assign owners, train relevant personnel and operate implemented controls.
Verify Measured And Managed Evidence
Test the effectiveness and consistency of measured and managed evidence.
Improve Remediation And Assessment Support
Close gaps and strengthen remediation and assessment support before the HITRUST assessment.
Evidence Commonly Prepared for HITRUST
The final evidence set depends on scope, risk, customer obligations and the selected HITRUST assessment route.
Typical HITRUST Records
- Scope, applicability and responsibility statement
- Assessment Scope And Factors register or criteria
- Csf Requirement Statements assessment records
- Policy And Procedure Maturity procedure or control matrix
- Implemented Controls operating evidence
- Measured And Managed Evidence monitoring or test results
- Remediation And Assessment Support review records
- Competence, awareness and communication evidence
- Internal review, findings and corrective-action log
- Management approval and HITRUST assessment readiness record
Weak Points to Correct Early
These issues commonly weaken HITRUST readiness or create avoidable questions during the HITRUST assessment.
- Defining assessment scope and factors without linking it to the real operating scope.
- Assigning no accountable owner for CSF requirement statements.
- Documenting policy and procedure maturity without current operating evidence.
- Leaving changes that affect implemented controls outside formal review.
- Approaching the HITRUST assessment before measured and managed evidence and remediation and assessment support have been tested.
Verified Jordan Resources for HITRUST Planning
Review CMMI certification guidance in Jordan for a verified Jordan process and capability resource connected to this programme.
Review ISO certification and sustainable growth across Jordan sectors for broader Jordan business and industry context.
Review a direct discussion about HITRUST implementation in Jordan to confirm scope, evidence needs and the appropriate assessment route.
HITRUST Questions from Jordan Organisations
These answers focus on scope, implementation evidence and preparation for the HITRUST assessment.
What business problem does HITRUST address for Jordan organisations?
It provides a structured way to organise healthcare and security requirements into a scoped, evidence-based HITRUST assessment programme while creating clear ownership and reviewable evidence.
Which Jordan operations usually consider HITRUST?
It is commonly relevant to Healthcare SaaS, Healthcare BPO, Hospitals and Provider Networks and other organisations with comparable assurance needs.
How should the scope for HITRUST be determined?
Scope should reflect the actual sites, services, products, systems, people and third parties needed for the HITRUST CSF assurance programme to achieve its intended outcome.
Why is assessment scope and factors important in HITRUST readiness?
Assessment scope and factors establishes the boundaries and decision criteria needed to make later controls and evidence coherent.
What evidence supports CSF requirement statements under HITRUST?
Evidence normally includes approved criteria, assigned responsibilities, operating records, monitoring results and actions taken when requirements are not met.
How is policy and procedure maturity checked before the HITRUST assessment?
Qualitcert reviews design, implementation and sampled evidence to confirm that policy and procedure maturity is applied consistently across the agreed scope.
Can HITRUST be coordinated with HIPAA?
Yes. Shared governance, risk, competence, document control, audit and improvement activities can often be aligned without losing service-specific requirements.
What common gap delays HITRUST readiness?
A frequent gap is having policies without current evidence that owners understand and operate the controls related to implemented controls.
What should management review before the HITRUST assessment for HITRUST?
Management should review scope, performance, open risks, findings, resources, changes and whether measured and managed evidence and remediation and assessment support are effective.
How does Qualitcert support HITRUST implementation in Jordan?
Qualitcert provides gap review, implementation planning, document and control development, training, internal review and readiness support without acting as the independent assessor.
Build a Practical HITRUST Programme in Jordan
Share your scope, current controls and target HITRUST assessment. Qualitcert can review gaps and define a proportionate implementation plan.