Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

tyre

Consulting &

ISO Certifications

-ISO Certification-

SOC II Certification Services in Tyre

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

For businesses handling sensitive data, SOC II (System and Organization Controls 2) certification is an essential compliance framework. Qualitcert provides professional SOC II certification services inTyre. Security, availability, processing integrity, confidentiality, and privacy are the five main trust service criteria that are the focus of this certification, which makes sure that companies put in place efficient controls to safeguard the data of their customers. The staff at Qualitcert inTyre offers comprehensive support, helping businesses navigate the intricate SOC II process from the first risk assessments and gap analyses to the creation of policies, audit planning, and final certification. Businesses may show their dedication to upholding strict data security and privacy requirements by earning SOC II accreditation. This is important for building confidence with stakeholders, partners, and clients in an increasingly data-driven environment.

Get In Touch

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

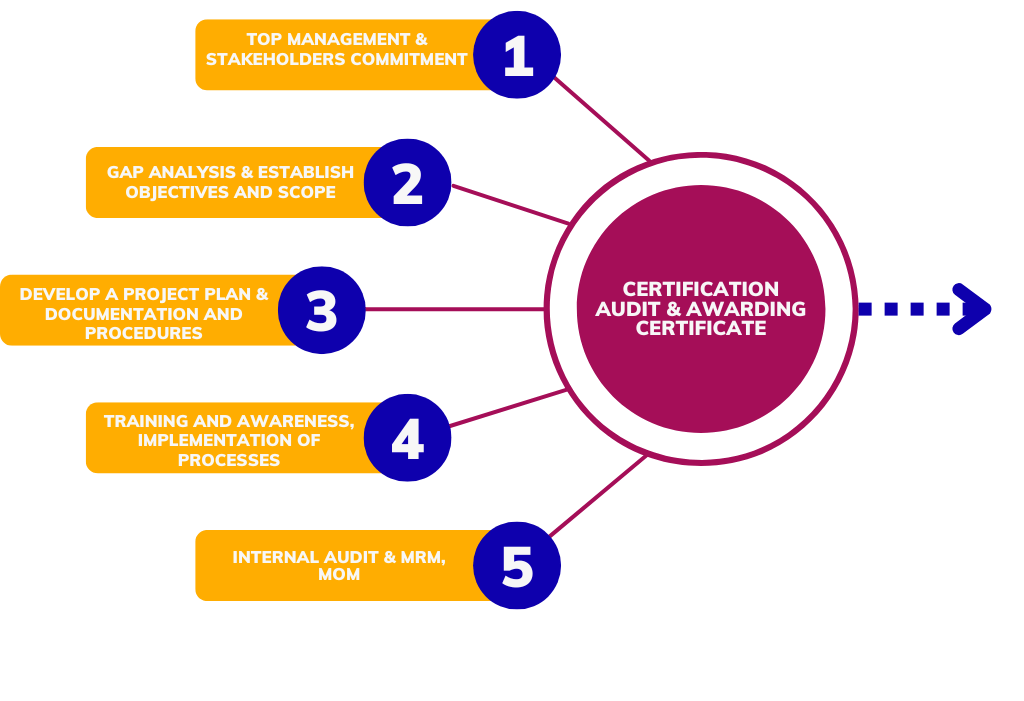
Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO  standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
Trust Assurance for Tyre Service Organisations

SOC 2 Certification Services in Tyre for Trust Services Criteria and Client Assurance

SOC 2 helps Tyre service organisations demonstrate controls for security, availability, processing integrity, confidentiality or privacy based on the Trust Services Criteria.

Prepare trust controls for technology-enabled services

SOC 2 certification services in Tyre are designed for service organisations that manage customer systems, data platforms, cloud environments, outsourced IT, software services or confidential client information.

The report is structured around the Trust Services Criteria. Security is the common category, while availability, processing integrity, confidentiality and privacy are added based on the services and client expectations.

SOC 2 readiness requires clear policies, access controls, change management, vendor oversight, incident response, monitoring evidence and control ownership.

Qualitcert supports Tyre organisations with SOC 2 gap review, criteria mapping, evidence planning, policy development, readiness remediation and preparation for Type I or Type II reporting.

Tyre Context

SOC 2 needs for Tyre service providers

Software teams, cloud service providers, managed IT firms, data processors and outsourced support organisations may face client due diligence requests for trust assurance.

SOC 2 helps service organisations respond with structured control evidence instead of separate questionnaire answers for every client.

The selected criteria should match real commitments. A company promising high availability, confidential processing or privacy controls needs evidence for those commitments.

Readiness work should also clarify the report boundary so systems, vendors, people and procedures are included only when they support the service description.

Operational Value

SOC 2 Benefits for Tyre Service Organisations

SOC 2 can support sales assurance, vendor due diligence and internal control maturity.

Stronger client trust

Customers receive structured assurance over selected trust criteria.

Better security governance

Access, monitoring, incidents and change controls become easier to evidence.

Reduced questionnaire fatigue

A report can answer many recurring customer control questions.

Clearer control ownership

Policies, evidence and responsibilities are assigned to accountable teams.

Sector Use

SOC 2 Applications in Tyre

SOC 2 is most useful where clients depend on the service provider’s systems or data controls.

01

Software-as-a-service providers

Application access, development changes and uptime commitments can be evidenced.

02

Managed IT service firms

Remote support, monitoring, ticketing and privileged access can be controlled.

03

Cloud hosting and platforms

Availability, logical access and incident response can be mapped.

04

Data processing providers

Confidentiality, privacy and processing integrity controls can be documented.

05

Fintech support services

Security controls and transaction processing commitments can be reviewed.

06

Customer support outsourcing

User access, data handling and confidentiality training can be included.

Preparation Route

SOC 2 Readiness Route

Preparation aligns the service description, selected criteria and evidence plan.

01

Define report boundary

Confirm services, systems, people, vendors and locations included.

02

Select criteria

Choose security and any additional Trust Services Criteria needed.

03

Map controls

Connect policies and activities to SOC 2 points of focus.

04

Review evidence

Check access reviews, change logs, incidents, monitoring and vendor records.

05

Remediate gaps

Strengthen controls before Type I or Type II reporting.

06

Prepare attestation

Organise narratives, control matrices and evidence for report readiness.

Evidence

SOC 2 Evidence Commonly Prepared

Evidence should show control design and, for Type II, operating effectiveness over time.

Typical SOC 2 Records

  • Service description
  • Trust criteria mapping
  • Information security policy
  • Access review records
  • Change management logs
  • Incident response records
  • Vendor risk reviews
  • Availability monitoring reports
  • Confidentiality agreements
  • Control owner matrix
SOC 2 evidence should be collected consistently throughout the report period.

SOC 2 Gaps to Avoid

These issues often slow SOC 2 readiness or weaken report confidence.

  • Selecting criteria that do not match client commitments.
  • Keeping policies without evidence that controls operate.
  • Not documenting privileged access review.
  • Ignoring vendors that support the service boundary.
  • Starting Type II before controls have operated consistently.
The report is stronger when each control has an owner, evidence source and review frequency.
Related Services

Information security governance can be strengthened through ISO 27001 ISMS certification services in Tyre.

Technical vulnerability evidence can support readiness through VAPT security testing company in Tyre.

Process documentation and corrective action discipline can be supported by ISO 9001 certification services in Tyre.

FAQs

SOC 2 Questions from Tyre Technology Providers

These answers explain Trust Services Criteria, report types and readiness evidence.

What is SOC 2 used for?

SOC 2 reports provide assurance over controls relevant to the Trust Services Criteria for service organisations.

What are the Trust Services Criteria?

They are security, availability, processing integrity, confidentiality and privacy criteria used to structure SOC 2 controls.

Is security always included in SOC 2?

Security is the common category, while the other criteria are selected based on service commitments and client needs.

What is SOC 2 Type I?

Type I reports on whether controls are suitably designed at a specific point in time.

What is SOC 2 Type II?

Type II reports on whether controls are suitably designed and operating effectively over a defined period.

How is SOC 2 different from ISO 27001?

SOC 2 is an attestation report based on Trust Services Criteria, while ISO 27001 is a certifiable ISMS standard based on risk management and Annex A controls.

What evidence is needed for SOC 2?

Evidence may include access reviews, change logs, incident records, monitoring reports, vendor reviews and policy acknowledgements.

Can small software companies prepare for SOC 2?

Yes, if control ownership, system boundaries and evidence collection are structured correctly.

Does SOC 2 require penetration testing?

It may not always be mandatory, but security testing can support control assurance and client expectations.

How does Qualitcert support SOC 2 in Tyre?

Qualitcert helps map criteria, review gaps, prepare policies and organise evidence for Type I or Type II readiness.

Speak with Qualitcert

Prepare SOC 2 Readiness in Tyre

Share your service model, systems and client control expectations. Qualitcert can help map SOC 2 criteria and evidence requirements.

Start SOC 2 Planning →
Scroll to Top