
An ISMS for real information risks, not just IT paperwork
ISO 27001 certification services in Zarqa begin by defining which information assets matter to the organization: customer records, financial data, production information, supplier contracts, employee files, ERP access, cloud accounts, backups, design files, network devices and service delivery data.
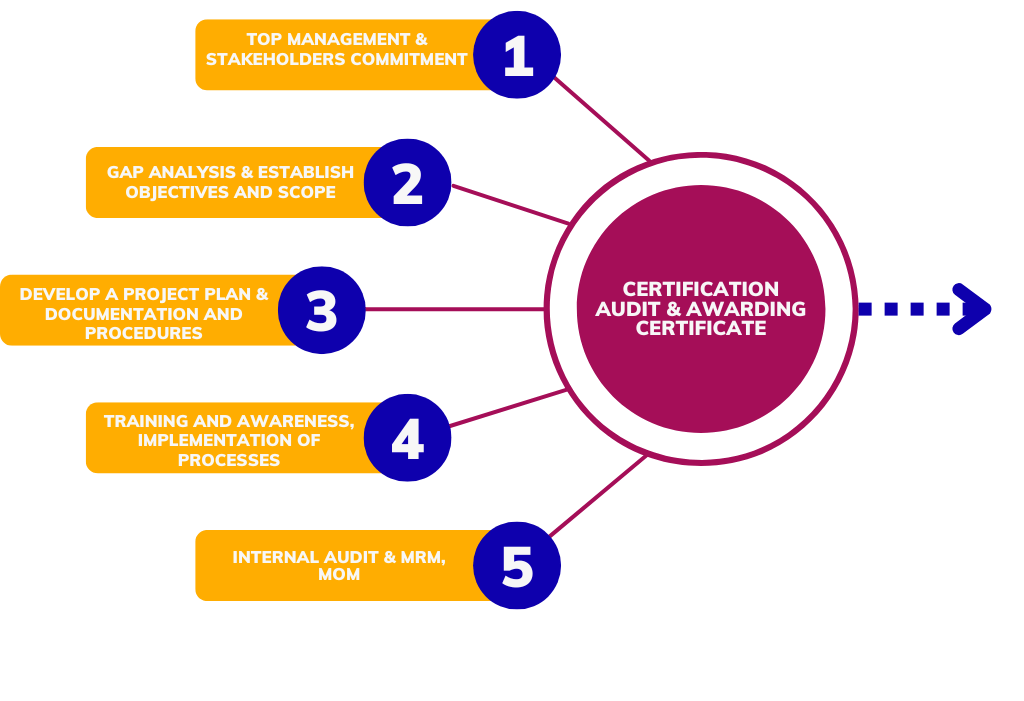
The standard requires an information security management system, commonly called an ISMS. It combines leadership, scope definition, risk assessment, risk treatment, documented policies, Annex A control implementation, internal audit, management review and continual improvement.
For manufacturers, service firms, logistics providers, medical suppliers, laboratories and technology-enabled businesses in Zarqa, information security is both a business continuity issue and a customer trust issue. A single access failure, ransomware incident, lost laptop, unprotected backup or supplier weakness can disrupt operations.
ISO 27001 implementation should be proportionate. A small service company may need controlled access, backup discipline and supplier clauses. A larger operation may need network segmentation, asset inventory, incident response, endpoint controls, logging, vulnerability management, business continuity planning and formal information security metrics.
Qualitcert helps organizations prepare the ISMS through gap analysis, scope definition, asset and risk registers, Statement of Applicability, policy framework, control implementation guidance, internal audit readiness, corrective action support and management review preparation.