
ISO Certifications
liberia
Consulting &
ISO Certifications

-ISO Certification-
ISO 27001 Certification Services in Liberia
QUALIT
CERT
CONSULTING AND ISO CERTIFICATIONS
Offering ISO 27001 certification services in Liberia, Qualitcert assists businesses in putting in place a strong Information Security Management System (ISMS) to protect confidential information and guarantee adherence to global standards. Businesses who want to control risk, safeguard their information assets, and win over customers by showcasing their dedication to data security must have the ISO 27001 accreditation. From the first evaluation and gap analysis to the complete implementation and audit preparation, Qualitcert offers professional advice at every stage of the procedure. Their services guarantee that Liberian businesses not only obtain ISO 27001 certification but also uphold ongoing development, adjust to changing security risks, and conform to international information security management best practices.
Get In Touch
Approach and Methodology used to implement Management System Standard
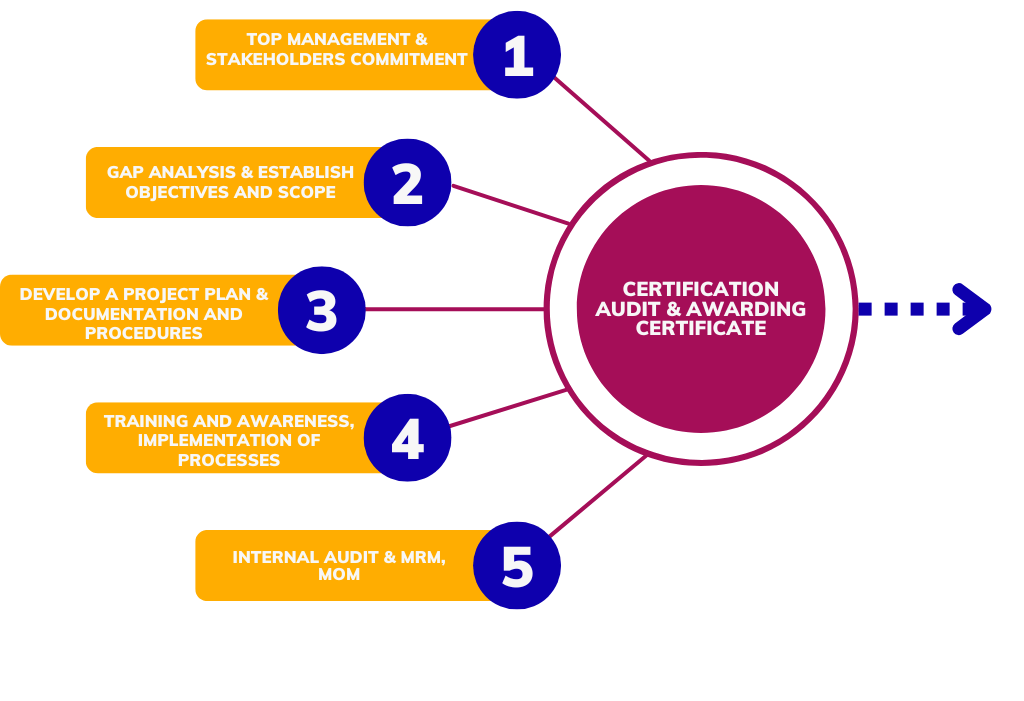
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
ISO 27001 Certification Services in Liberia for Risk-Based Information Security
ISO/IEC 27001 helps Liberian organisations protect information through a scoped ISMS, formal risk treatment and evidence-based Annex A controls.
Connect business risk with technical and organisational security controls
ISO/IEC 27001 specifies requirements for establishing, implementing, maintaining and continually improving an information security management system. It requires defined scope, leadership, risk assessment, risk treatment and performance evaluation.
Banks, mobile-money providers, telecom operators, public institutions and digital-service providers in Liberia depend on cloud platforms, remote access, third parties and interconnected applications.
A defensible ISMS identifies information assets, threats, vulnerabilities and business consequences before selecting controls. The Statement of Applicability then explains which Annex A controls are relevant, implemented or excluded and why.
Qualitcert supports scope definition, risk methodology, asset registers, policies, supplier controls, incident readiness, internal audit and certification preparation.
Security assurance for Liberia's financial, public and digital services
Digital transactions, customer data and outsourced technology require consistent information security responsibilities and evidence.
Access control, privileged administration, secure configuration and change management should reflect actual architecture. Generic policies are insufficient without approvals, logs and periodic reviews.
Supplier and cloud risks require clear responsibility for data handling, incident notification, continuity and exit arrangements. Contracts should align with risk-treatment decisions.
Mobile services, public portals and industrial environments also require tested incident response, backup, recovery and communication arrangements.
How ISO 27001 supports trust and resilience
The value lies in making security decisions traceable, risk-based and repeatable across business and technical teams.
Better risk ownership
Business owners can see residual risk, treatment status and the decisions requiring acceptance or investment.
Stronger customer assurance
Controlled evidence supports due diligence, tenders and security reviews from clients and partners.
More coordinated incident response
Roles, escalation, evidence handling and lessons learned are planned before a security event occurs.
Improved supplier governance
Security expectations, assessments and monitoring are aligned with the information and services entrusted to third parties.
ISO 27001 applications in Liberia's service economy
The scope and controls should reflect information flows, technology dependencies and contractual commitments.
Banking and mobile money
Protect customer information, payment systems, privileged access, interfaces and incident evidence.
Telecommunications
Govern subscriber data, network administration, platforms and third-party access.
Government digital services
Secure citizen information, portals, shared systems and outsourced processing.
Mining and port operations
Coordinate corporate IT, operational technology, remote support and supplier controls.
Cloud and software providers
Manage secure development, logging, vulnerability handling and continuity.
Healthcare and insurance
Protect sensitive records, claims data, user access and service dependencies.
From scope and risk assessment to an auditable ISMS
ISO 27001 implementation works best when risk treatment and operational evidence are developed together.
Define the ISMS boundary
Confirm sites, services, systems, people, interfaces and exclusions that shape the certification scope.
Establish risk methodology
Set criteria for likelihood, impact, acceptance, ownership and consistent information-security risk evaluation.
Assess and treat risks
Identify assets, threats and vulnerabilities, then select avoidance, modification, sharing or acceptance options.
Implement Annex A controls
Prepare the Statement of Applicability and operate selected organisational, people, physical and technological controls.
Measure and challenge
Monitor objectives, incidents, supplier performance, vulnerabilities and control effectiveness through internal audit.
Review and certify
Complete management review, corrective actions and evidence preparation for the certification audit stages.
Policies, registers and records expected during ISO 27001 assessment
Documentation should explain the organisation's security logic and provide evidence that selected controls are operating.
Common ISMS records
- ISMS scope and policy
- Risk assessment methodology
- Information risk register
- Risk treatment plan
- Statement of Applicability
- Asset and access records
- Supplier security assessments
- Incident response records
- Internal audit programme
- Management review minutes
ISMS mistakes that weaken assurance
Certification problems often arise when technical controls exist but governance, risk reasoning or operating evidence is incomplete.
- Copying a generic risk register that does not reflect real services and information flows.
- Selecting all Annex A controls without documenting applicability and treatment rationale.
- Restricting the ISMS to IT while business owners and suppliers remain outside the process.
- Listing policies without retaining logs, reviews, approvals or test evidence.
- Accepting residual risk informally without defined authority or review dates.
Related ISO/IEC 27001 Services for Liberian Organisations
For a connected requirement, review SOC 2 certification services in Liberia to coordinate shared governance, documentation and management responsibilities.
For a connected requirement, review VAPT certification services in Liberia where common risks, suppliers or operational controls should be aligned.
For a connected requirement, review ISO 9001 certification services in Liberia to reduce duplicated work and build a coherent assurance programme.
ISO 27001 questions from Liberia-based organisations
These answers focus on risk assessment, Annex A, scope, evidence and certification.
What is an Information Security Management System?
An ISMS is a coordinated set of policies, risk processes, responsibilities, controls and reviews used to protect information and improve security performance.
Does ISO 27001 require every Annex A control?
No. The organisation considers all Annex A controls, but selects those needed based on risk treatment and other requirements, documenting decisions in the Statement of Applicability.
What is the Statement of Applicability?
It records control applicability, justification, implementation status and references, providing a bridge between risk treatment and the Annex A control set.
Can a cloud-based company be certified to ISO 27001?
Yes. The organisation must define its scope and manage shared responsibilities, suppliers, access, configuration, monitoring, backup and incident obligations.
How detailed should the information risk register be?
It should be detailed enough to support consistent decisions, clear ownership, treatment tracking and residual risk acceptance without becoming unmanageable.
Is penetration testing mandatory for ISO 27001?
The standard does not prescribe one universal test schedule, but vulnerability and security testing may be necessary based on risk, contractual duties and selected controls.
How are suppliers included in an ISMS?
Suppliers are assessed according to the information, systems and services they affect, with security requirements, monitoring and exit arrangements defined as appropriate.
What is the difference between risk assessment and risk treatment?
Assessment identifies and evaluates risk. Treatment decides what to do about it, assigns actions, selects controls and documents residual risk.
Can ISO 27001 support client security questionnaires?
Yes. A controlled ISMS provides policies, risk records, audits, incident processes and control evidence that can make due diligence more consistent.
How does Qualitcert support ISO 27001 in Liberia?
Qualitcert can help define scope, create the risk framework, prepare the Statement of Applicability, document controls, audit the ISMS and prepare for certification.
Define an ISO 27001 Readiness Plan for Your Liberia Organisation
Share your scope, systems, risk method and current policies. Qualitcert can help structure the ISMS, Annex A evidence and audit roadmap.