









Global ISO Certification Consultant Services – Qualitcert

QualitCert Get a Quote

ISO Certifications

chile

Consulting &

ISO Certifications

-ISO Certification-

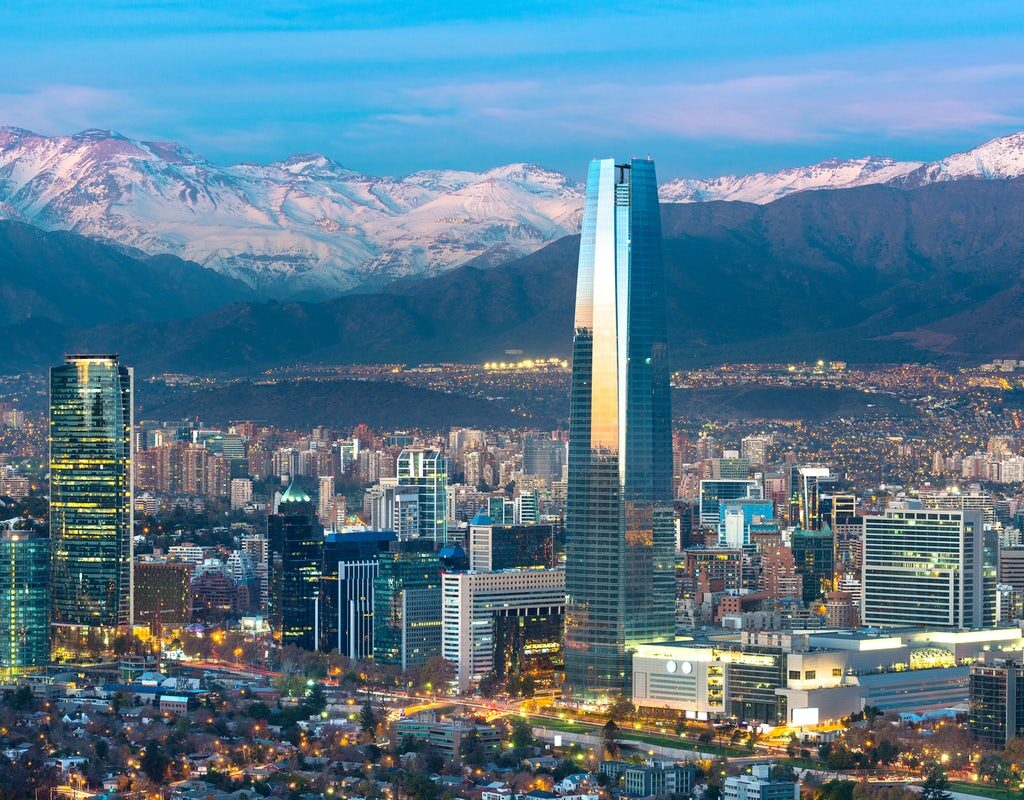
ISO 27001 Certification Consulting Services in Chile

QUALIT

CERT

CONSULTING AND ISO CERTIFICATIONS

Qualitcert provides ISO 27001 certification consulting services in Chile to help firms improve their information security management systems (ISMS) and bring them into compliance with global standards. For companies looking to protect sensitive information, ISO 27001 is essential since it guarantees information availability, confidentiality, and integrity. To satisfy the standards, Qualitcert offers end-to-end consulting services that include gap analyses, risk assessments, policy creation, and training. Their professionals assist businesses with the certification process, ensuring that all security measures are implemented and in line with organizational goals. Whether you work in the financial, healthcare, IT, or other industries, ISO 27001 compliance protects your brand, minimizes security breaches, and fosters client and stakeholder trust. Businesses in Chile can confidently pursue certification while strengthening their security posture and complying by working with Qualitcert.

Get In Touch

Test
Consultants Consultants
afd9a249 perf wp theme group 8796 Consultants Consultants

Approach and Methodology used to implement Management System Standard

Colorful Minimalist Linear Steps Circular Diagram 1 e1712599893569 Consultants Consultants

Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework

Ellipse 6 copy Consultants Consultants

OUR

Process

1, Determine the ISO Standard

2. Understand the Requirements

3. Training and Awareness

4. Implement the System

5. Internal Audit

6. Certification

partner_img Consultants Consultants

Benefits of having ISO Certification

Enhanced Credibility and Reputation

Legal and Regulatory Compliance

Enhanced Customer Satisfaction

Access to Global Markets

Environmental Sustainability

Information Security

Our Achievements and Success

Professional Experts
0 +
Years Experience
0 +
Projects
0 +
Satisfied Customers
0 %

Our Clients

WhatsApp Image 2023 05 12 at 8.24.31 PM e1684164170667
WhatsApp Image 2023 05 12 at 8.16.53 PM e1684163940587
WhatsApp Image 2023 05 12 at 8.22.55 PM
WhatsApp Image 2023 05 12 at 8.04.13 PM 3 e1684163886384
WhatsApp Image 2023-05-12 at 8.15.32 PM

OUR

SERVICES

ISO 9001 Certification
ISO 45001 Certification
ISO 14001 Certification
ISO 22000 Certification
ISO 13485 Certification
ISO 27001 Certification
ISO 20000-1 Certification
ISO 29001 Certification
System Design and Evidence

Turning ISO/IEC 27001 requirements into working controls in Chile

For the ISO/IEC 27001 scope in Chile, ISO/IEC 27001 preparation should create a system that people can operate and an auditor can trace. The focus here is make information-security decisions traceable from business risk through control selection and continual improvement.

Where ISO/IEC 27001 preparation usually succeeds or fails

ISO/IEC 27001 readiness in Chile depends on evidence that the management approach works under normal pressure, during change and when something goes wrong. The central objective is to make information-security decisions traceable from business risk through control selection and continual improvement.

This matters for technology companies, managed service providers, financial-support operations, engineering firms and data-intensive businesses, where customer expectations and operational risks can cross departmental boundaries. For this ISO/IEC 27001 page in Chile, in the Chile implementation context, A well-designed system gives each process owner a clear basis for making and recording decisions.

Typical weak points involve cloud dependency, privileged access, third-party services, remote work and inconsistent incident escalation. For this ISO/IEC 27001 page in Chile, within Chile's defined certification boundary, these issues are easier to correct when they are found during structured implementation rather than during the final certification audit.

Qualitcert supports the preparation of a coherent evidence trail covering risk assessments, Statement of Applicability, access reviews, security monitoring and supplier-risk records. For teams maintaining ISO/IEC 27001 in Chile, the emphasis stays on useful controls, accountable ownership and records that explain what actually happened.

Business Environment

How ISO/IEC 27001 fits the operating reality in Chile

A useful system reflects real process boundaries, external dependencies and the risks created by technology companies, managed service providers, financial-support operations, engineering firms and data-intensive businesses.

The operating context in Chile shapes how ISO/IEC 27001 should be implemented. Organizations working across technology companies, managed service providers, financial-support operations, engineering firms and data-intensive businesses may share the same standard, but their risks, evidence and process boundaries are not interchangeable.

For the ISO/IEC 27001 scope in Chile, A sensible implementation starts by separating what already works from what is only informal. Particular attention should be given to cloud dependency, privileged access, third-party services, remote work and inconsistent incident escalation, because these areas can affect customers, regulators, workers or delivery performance depending on the standard.

Readiness improves when the management team can explain why controls exist and can show recent records such as risk assessments, Statement of Applicability, access reviews, security monitoring and supplier-risk records. For this ISO/IEC 27001 page in Chile, in the Chile implementation context, that makes the system easier to audit and easier to maintain after certification.

Management Value

Within Chile's defined certification boundary, what ISO/IEC 27001 can improve beyond the certificate

For teams maintaining ISO/IEC 27001 in Chile, the strongest outcomes are visible in decisions, handovers, monitoring and corrective action—not in certificate wording alone.

Risk ownership

Security risks receive named owners, treatment decisions and review dates instead of remaining in an informal issue list, for teams maintaining the ISO/IEC 27001 controls in Chile. A useful test is whether this control helps technology companies handle cloud dependency without creating a parallel paperwork process.

Control traceability

The Statement of Applicability explains why controls are selected, excluded or adapted to the organization, inside the auditable ISO/IEC 27001 boundary in Chile. A useful test is whether this control helps managed service providers handle privileged access without creating a parallel paperwork process.

Customer assurance

Evidence can be presented more consistently during supplier-security reviews and contract due diligence, for the operating conditions included in the Chile scope. A useful test is whether this control helps financial-support operations handle third-party services without creating a parallel paperwork process.

Incident learning

Security events feed corrective action, control improvement and management review rather than ending with technical recovery, within the defined ISO/IEC 27001 scope in Chile. A useful test is whether this control helps engineering firms handle remote work without creating a parallel paperwork process.

Application Examples

Where ISO/IEC 27001 is applied across Chile

In practical ISO/IEC 27001 use across Chile, the same standard can demand different evidence depending on process risk, product or service type, workforce and customer expectations.

01

Technology delivery

Protect source code, development environments, credentials and customer data across delivery teams, inside the auditable ISO/IEC 27001 boundary in Chile. In Chile, the implementation can be tailored around privileged access, with records scaled to the complexity of the operation.

02

Managed services

Define access, monitoring, escalation and third-party controls for services operated on behalf of customers, for the operating conditions included in the Chile scope. In Chile, the implementation can be tailored around third-party services, with records scaled to the complexity of the operation.

03

Financial support

Strengthen confidentiality, privileged access and continuity controls around sensitive business information, within the defined ISO/IEC 27001 scope in Chile. In Chile, the implementation can be tailored around remote work, with records scaled to the complexity of the operation.

04

Engineering offices

Control project data, shared platforms, remote access and external collaboration, for the Chile operation covered by this ISO/IEC 27001 work. In Chile, the implementation can be tailored around inconsistent incident escalation, with records scaled to the complexity of the operation.

05

Professional services

Apply risk-based controls to client files, cloud applications and mobile work, as part of the ISO/IEC 27001 system used in Chile. In Chile, the implementation can be tailored around cloud dependency, with records scaled to the complexity of the operation.

06

Data operations

Connect retention, access review, backup, logging and incident response to defined information risks, for teams maintaining the ISO/IEC 27001 controls in Chile. In Chile, the implementation can be tailored around privileged access, with records scaled to the complexity of the operation.

Preparation Framework

For the ISO/IEC 27001 scope in Chile, A six-stage route from current practice to ISO/IEC 27001 readiness

In the Chile implementation context, each stage should leave the organization with a stronger operating control, not just another document.

01

Define the ISMS boundary

Confirm business units, locations, systems, interfaces and interested parties included in scope, for teams maintaining the ISO/IEC 27001 controls in Chile. The checkpoint should be tested using recent evidence from financial-support operations rather than relying on a newly written procedure.

02

Assess information risk

Identify assets, threats, vulnerabilities, impacts and existing safeguards using an agreed method, inside the auditable ISO/IEC 27001 boundary in Chile. The checkpoint should be tested using recent evidence from engineering firms rather than relying on a newly written procedure.

03

Plan risk treatment

Select treatment options, assign owners and connect decisions to the Statement of Applicability, for the operating conditions included in the Chile scope. The checkpoint should be tested using recent evidence from data-intensive businesses rather than relying on a newly written procedure.

04

Implement governance

Establish policies, operating controls, competence, supplier oversight and incident responsibilities, within the defined ISO/IEC 27001 scope in Chile. The checkpoint should be tested using recent evidence from technology companies rather than relying on a newly written procedure.

05

Test effectiveness

Use internal audit, access review, monitoring, exercises and corrective action to test the system, for the Chile operation covered by this ISO/IEC 27001 work. The checkpoint should be tested using recent evidence from managed service providers rather than relying on a newly written procedure.

06

Prepare for certification

Complete management review, close significant gaps and organize objective evidence for the audit, as part of the ISO/IEC 27001 system used in Chile. The checkpoint should be tested using recent evidence from financial-support operations rather than relying on a newly written procedure.

Evidence Pack

Within Chile's defined certification boundary, records that make ISO/IEC 27001 implementation auditable

For teams maintaining ISO/IEC 27001 in Chile, documents matter when they support decisions and prove implementation; uncontrolled templates add volume without strengthening assurance.

Core evidence set

  • ISMS scope statement
  • Information security policy
  • Risk assessment method
  • Risk register
  • Risk treatment plan
  • Statement of Applicability
  • Asset or information inventory
  • Supplier security records
  • Incident and event records
  • Internal audit and management review
Evidence should be current, attributable and consistent with the defined ISO/IEC 27001 scope in Chile. In this ISO/IEC 27001 implementation for Chile, where several records support the same decision, keep ownership and revision status clear so an auditor can follow the trail without reconstruction.

Weaknesses that undermine readiness

In practical ISO/IEC 27001 use across Chile, these issues commonly reduce confidence in implementation because they separate written requirements from the way work is actually controlled.

  • Treating the control list as a checklist without a documented risk rationale, within the defined ISO/IEC 27001 scope in Chile.
  • Writing a broad scope that does not match the systems and teams actually managed, for the Chile operation covered by this ISO/IEC 27001 work.
  • Keeping supplier security obligations outside the risk and monitoring process, as part of the ISO/IEC 27001 system used in Chile.
  • Failing to demonstrate that access reviews and incident actions are completed, for teams maintaining the ISO/IEC 27001 controls in Chile.
  • Using policies as evidence when operating records do not show implementation, inside the auditable ISO/IEC 27001 boundary in Chile.
For the ISO/IEC 27001 scope in Chile, closing a systemic cause is more valuable than polishing wording immediately before the ISO/IEC 27001 audit. Prioritize gaps that affect cloud dependency, privileged access, third-party services, remote work and inconsistent incident escalation before spending time on cosmetic document formatting.
Complementary Services

Within Chile's defined certification boundary, where the same teams own overlapping controls, reviewISO/IEC 27701. For teams maintaining ISO/IEC 27001 in Chile, keep the scopes distinct while reusing genuinely shared evidence such as competence, audit, supplier or management-review records where appropriate.

In practical ISO/IEC 27001 use across Chile, if the organization is coordinating adjacent assurance work, reviewISO 22301. For the ISO/IEC 27001 scope in Chile, keep the scopes distinct while reusing genuinely shared evidence such as competence, audit, supplier or management-review records where appropriate.

In the Chile implementation context, for a connected requirement with shared records, reviewISO/IEC 20000-1. For this ISO/IEC 27001 page in Chile, within Chile's defined certification boundary, keep the scopes distinct while reusing genuinely shared evidence such as competence, audit, supplier or management-review records where appropriate.

Practical FAQs

ISO/IEC 27001 questions organizations in Chile often raise

For teams maintaining ISO/IEC 27001 in Chile, these answers focus on implementation choices, evidence and audit readiness rather than generic definitions.

How should the ISO/IEC 27001 scope be defined for an organization in Chile?

In practical ISO/IEC 27001 use across Chile, the scope should clearly identify organizational units, locations, information, technology and interfaces that the ISMS controls. For the ISO/IEC 27001 scope in Chile, exclusions or external dependencies need to be understandable from the scope and supporting context analysis. For Chile, the practical check is whether the answer is supported by current records from technology companies.

When preparing ISO/IEC 27001 in Chile, is a Statement of Applicability enough to show compliance?

No. Within Chile's defined certification boundary, the Statement of Applicability records control decisions, but auditors also look for evidence that selected controls are implemented, monitored and reviewed. For teams maintaining ISO/IEC 27001 in Chile, the records should reflect the actual scope and operating arrangements used in Chile. For Chile, the practical check is whether the answer is supported by current records from managed service providers.

Within a ISO/IEC 27001 project in Chile, what is the difference between a risk register and a risk treatment plan?

For the ISO/IEC 27001 scope in Chile, the risk register records assessed information-security risks. In the Chile implementation context, the treatment plan records what will be done, who owns the action, target dates and how residual risk will be handled. For Chile, the practical check is whether the answer is supported by current records from financial-support operations.

For organizations in Chile, do cloud suppliers need to be inside the ISMS?

For teams maintaining ISO/IEC 27001 in Chile, their services and associated risks should be addressed when they affect information within scope, even when the supplier itself is not part of the organization. For Chile, the practical check is whether the answer is supported by current records from engineering firms.

What evidence is useful before Stage 1 before certification work in Chile?

In practical ISO/IEC 27001 use across Chile, A defined scope, core policies, risk methodology, current risk assessment, treatment plan, Statement of Applicability and evidence that the ISMS has started operating are important foundations. For Chile, the practical check is whether the answer is supported by current records from data-intensive businesses.

What should internal audit test?

For the ISO/IEC 27001 scope in Chile, internal audit should test both conformity and effectiveness: whether required arrangements exist, whether teams follow them and whether the controls achieve their intended purpose. For this ISO/IEC 27001 page in Chile, in the Chile implementation context, the records should reflect the actual scope and operating arrangements used in Chile. For Chile, the practical check is whether the answer is supported by current records from technology companies.

Within a ISO/IEC 27001 project in Chile, how are incidents handled under ISO/IEC 27001?

For teams maintaining ISO/IEC 27001 in Chile, the organization should have defined reporting, response, learning and corrective-action arrangements proportionate to its risks and operations. For Chile, the practical check is whether the answer is supported by current records from managed service providers.

For the Chile certification scope, can ISO/IEC 27001 support customer security reviews?

Yes. For the ISO/IEC 27001 scope in Chile, A functioning ISMS can provide structured evidence about governance, risk treatment, supplier control, incident management and continual improvement. For Chile, the practical check is whether the answer is supported by current records from financial-support operations.

How often should risks be reviewed?

In the Chile implementation context, risk review frequency should be defined by the organization and should also respond to significant changes, incidents, new technologies or business requirements. For this ISO/IEC 27001 page in Chile, within Chile's defined certification boundary, the records should reflect the actual scope and operating arrangements used in Chile. For Chile, the practical check is whether the answer is supported by current records from engineering firms.

How can Qualitcert support ISO/IEC 27001 readiness in Chile?

For teams maintaining ISO/IEC 27001 in Chile, qualitcert can review scope, current controls, risk documentation, evidence quality, internal-audit readiness and management-review inputs before certification assessment. For Chile, the practical check is whether the answer is supported by current records from data-intensive businesses.

Build a Clear Roadmap

In practical ISO/IEC 27001 use across Chile, turn your current ISO/IEC 27001 work into a clear readiness plan

For the ISO/IEC 27001 scope in Chile, share your current scope, key processes and available records. Qualitcert can help identify the priority gaps and organize a practical ISO/IEC 27001 readiness route for Chile.

Request a Readiness Review →
Scroll to Top