
ISO Certifications
Riy
adh
Consulting &
ISO Certifications
-ISO Certification-
ISO 20000 Certification Services in Riyadh
QUALIT
CERT
CONSULTING AND ISO CERTIFICATIONS
In Riyadh, QualitCert offers ISO 20000 Certification services, assisting businesses in putting in place an excellent ITSM that complies with global standards. Businesses looking to increase customer happiness, provide dependable and effective IT services, and guarantee constant service quality must have ISO 20000 certification. From doing initial assessments and detecting service gaps to implementing simplified procedures and best practices in IT service management, our knowledgeable staff at QualitCert helps firms navigate every step of the certification process. Businesses in Riyadh may enhance their IT service delivery, minimize downtime, and forge closer bonds with clients by obtaining ISO 20000 certification with QualitCert, which shows a dedication to IT service excellence and ongoing development.
Get In Touch
Approach and Methodology used to implement Management System Standard
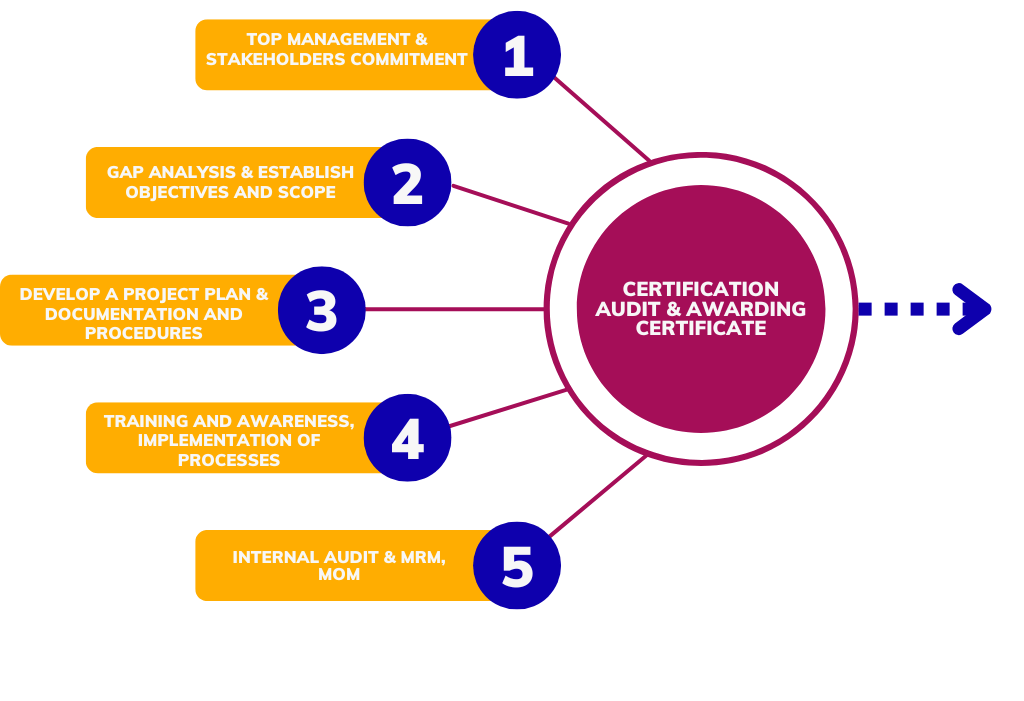
Implementing an ISO standards involves a structured methodology to ensure that the organization effectively meets the requirements of the chosen standard and achieves certification. Sometimes defined methodology may vary depending on factors such as the size of the organization, its industry, and the complexity of the ISO standard being implemented, the following steps provide a basic framework
OUR
Process
1, Determine the ISO Standard
2. Understand the Requirements
3. Training and Awareness
4. Implement the System
5. Internal Audit
6. Certification
Benefits of having ISO Certification
Enhanced Credibility and Reputation
Legal and Regulatory Compliance
Enhanced Customer Satisfaction
Access to Global Markets
Environmental Sustainability
Information Security
Our Achievements and Success
Our Clients
OUR
SERVICES
ISO/IEC 20000-1 Consulting and Readiness Services in Riyadh
Build a practical IT service management system that helps Riyadh organisations manage the planning, delivery, support and continual improvement of reliable IT services with clear ownership, current evidence and assessment readiness.
Make IT Service Commitments Measurable and Repeatable
Managed IT, cloud, enterprise-support and digital-service teams in Riyadh need service controls that remain reliable during rapid operational change. Managed IT, cloud, enterprise-support and technical-service teams in Riyadh need service controls that remain reliable during operational change. Managed IT, cloud, enterprise-support and technical-service teams in Riyadh need service controls that remain reliable during operational change. Managed IT, cloud, enterprise-support and technical-service teams in Riyadh need service controls that remain reliable during operational change. Managed IT, cloud, enterprise-support and technical-service teams in Riyadh need service controls that remain reliable during operational change. Managed IT, cloud, industrial-support and enterprise technology teams in Riyadh need service controls that remain reliable during operational change. Managed IT, cloud, data-centre and enterprise-support teams in Riyadh need service controls that remain reliable during rapid change. Managed IT, cloud, data-centre and enterprise support teams in Riyadh need service controls that remain reliable during rapid change and customer growth. ISO/IEC 20000-1 is most useful when it improves business decisions rather than creating a parallel documentation system. Its purpose is to manage the planning, delivery, support and continual improvement of reliable IT services.
For Riyadh organisations, the implementation often needs to bridge specialist functions, outsourced activities and fast-changing customer requirements.
Qualitcert therefore builds the IT service management system around the operating reality of service management scope, service portfolio and catalogue, service levels and incident and request management, with clear owners and review points.
Evidence for change and release control and continual improvement is then tested through internal review before the certification audit, helping the system remain useful after the formal assessment.
Service Management for Riyadh's Managed IT and Digital Operations
Riyadh organisations use ISO/IEC 20000-1 to improve assurance where service management scope, service portfolio and catalogue and service levels cross teams, suppliers or technical systems.
Customers in Riyadh expect reliable digital and technical services across cloud, workplace, network, helpdesk and managed-operation environments.
That operating model makes consistent control of service management scope, service portfolio and catalogue and service levels important for both daily performance and external assurance.
The programme therefore emphasises usable evidence for incident and request management, change and release control and continual improvement across the exact activities included in scope.
Operational Benefits of ISO/IEC 20000-1 in Riyadh
The value comes from making service management scope, service portfolio and catalogue and service levels easier to manage, measure and explain.
Clearer Service Management Scope
Defines ownership, criteria and evidence for service management scope across the agreed scope.
Stronger Service Portfolio And Catalogue
Connects service portfolio and catalogue to practical controls rather than isolated policy statements.
More Reliable Service Levels
Makes service levels easier to monitor, test and improve with current records.
Better Incident And Request Management
Supports consistent decisions about incident and request management during normal work and change.
Where ISO/IEC 20000-1 Applies in Riyadh
The examples below show how the IT service management system changes with the operating model, risk profile and evidence needs of each sector.
Managed IT and Enterprise Support
Control service levels, incidents, changes, capacity, suppliers and customer reporting.
SaaS Operations Teams
Link platform commitments with support, availability, release and problem management.
Data Centres
Control service continuity, capacity, incidents, changes and customer communication.
Enterprise IT Functions
Standardise internal services, ownership, demand, support and performance review.
Telecom and Network Services
Manage service availability, events, changes, suppliers and restoration.
Technical Support Centres
Improve request handling, escalation, knowledge, closure and satisfaction monitoring.
How ISO/IEC 20000-1 Readiness Is Built
The sequence moves from scope and current-state review to operating evidence and preparation for the certification audit.
Define Service Management Scope
Confirm boundaries, responsibilities and criteria for service management scope.
Assess Service Portfolio And Catalogue
Review current practices, risks and evidence relating to service portfolio and catalogue.
Design Service Levels
Create proportionate controls and records for service levels.
Implement Incident And Request Management
Assign owners, train relevant personnel and operate incident and request management.
Verify Change And Release Control
Test the effectiveness and consistency of change and release control.
Improve Continual Improvement
Close gaps and strengthen continual improvement before the certification audit.
Evidence Commonly Prepared for ISO/IEC 20000-1
The final evidence set depends on scope, risk, customer obligations and the selected certification audit route.
Typical ISO/IEC 20000-1 Records
- Scope, applicability and responsibility statement
- Service Management Scope register or criteria
- Service Portfolio And Catalogue assessment records
- Service Levels procedure or control matrix
- Incident And Request Management operating evidence
- Change And Release Control monitoring or test results
- Continual Improvement review records
- Competence, awareness and communication evidence
- Internal review, findings and corrective-action log
- Management approval and certification audit readiness record
Weak Points to Correct Early
These issues commonly weaken ISO/IEC 20000-1 readiness or create avoidable questions during the certification audit.
- Defining service management scope without linking it to the real operating scope.
- Assigning no accountable owner for service portfolio and catalogue.
- Documenting service levels without current operating evidence.
- Leaving changes that affect incident and request management outside formal review.
- Approaching the certification audit before change and release control and continual improvement have been tested.
Verified Saudi Arabia Resources for ISO/IEC 20000-1 Planning
Review ISO certification and sustainable growth across Saudi Arabia for verified national business and sector context relevant to Riyadh organisations.
Review Qualitcert services to review the broader consulting and compliance support portfolio.
Review a direct discussion about ISO/IEC 20000-1 implementation in Riyadh to confirm scope, evidence needs and the appropriate assessment route.
ISO/IEC 20000-1 Questions from Riyadh Organisations
These answers focus on scope, implementation evidence and preparation for the certification audit.
What business problem does ISO/IEC 20000-1 address for Riyadh organisations?
It provides a structured way to manage the planning, delivery, support and continual improvement of reliable IT services while creating clear ownership and reviewable evidence.
Which Riyadh operations usually consider ISO/IEC 20000-1?
It is commonly relevant to Managed IT Service Providers, SaaS Operations Teams, Data Centres and other organisations with comparable assurance needs.
How should the scope for ISO/IEC 20000-1 be determined?
Scope should reflect the actual sites, services, products, systems, people and third parties needed for the IT service management system to achieve its intended outcome.
Why is service management scope important in ISO/IEC 20000-1 readiness?
Service management scope establishes the boundaries and decision criteria needed to make later controls and evidence coherent.
What evidence supports service portfolio and catalogue under ISO/IEC 20000-1?
Evidence normally includes approved criteria, assigned responsibilities, operating records, monitoring results and actions taken when requirements are not met.
How is service levels checked before the certification audit?
Qualitcert reviews design, implementation and sampled evidence to confirm that service levels is applied consistently across the agreed scope.
Can ISO/IEC 20000-1 be coordinated with ISO/IEC 27001?
Yes. Shared governance, risk, competence, document control, audit and improvement activities can often be aligned without losing service-specific requirements.
What common gap delays ISO/IEC 20000-1 readiness?
A frequent gap is having policies without current evidence that owners understand and operate the controls related to incident and request management.
What should management review before the certification audit for ISO/IEC 20000-1?
Management should review scope, performance, open risks, findings, resources, changes and whether change and release control and continual improvement are effective.
How does Qualitcert support ISO/IEC 20000-1 implementation in Riyadh?
Qualitcert provides gap review, implementation planning, document and control development, training, internal review and readiness support without acting as the independent assessor.
Build a Practical ISO/IEC 20000-1 Programme in Riyadh
Share your scope, current controls and target certification audit. Qualitcert can review gaps and define a proportionate implementation plan.